Testing OAuth 2.0 Implementations: A Developer's Guide
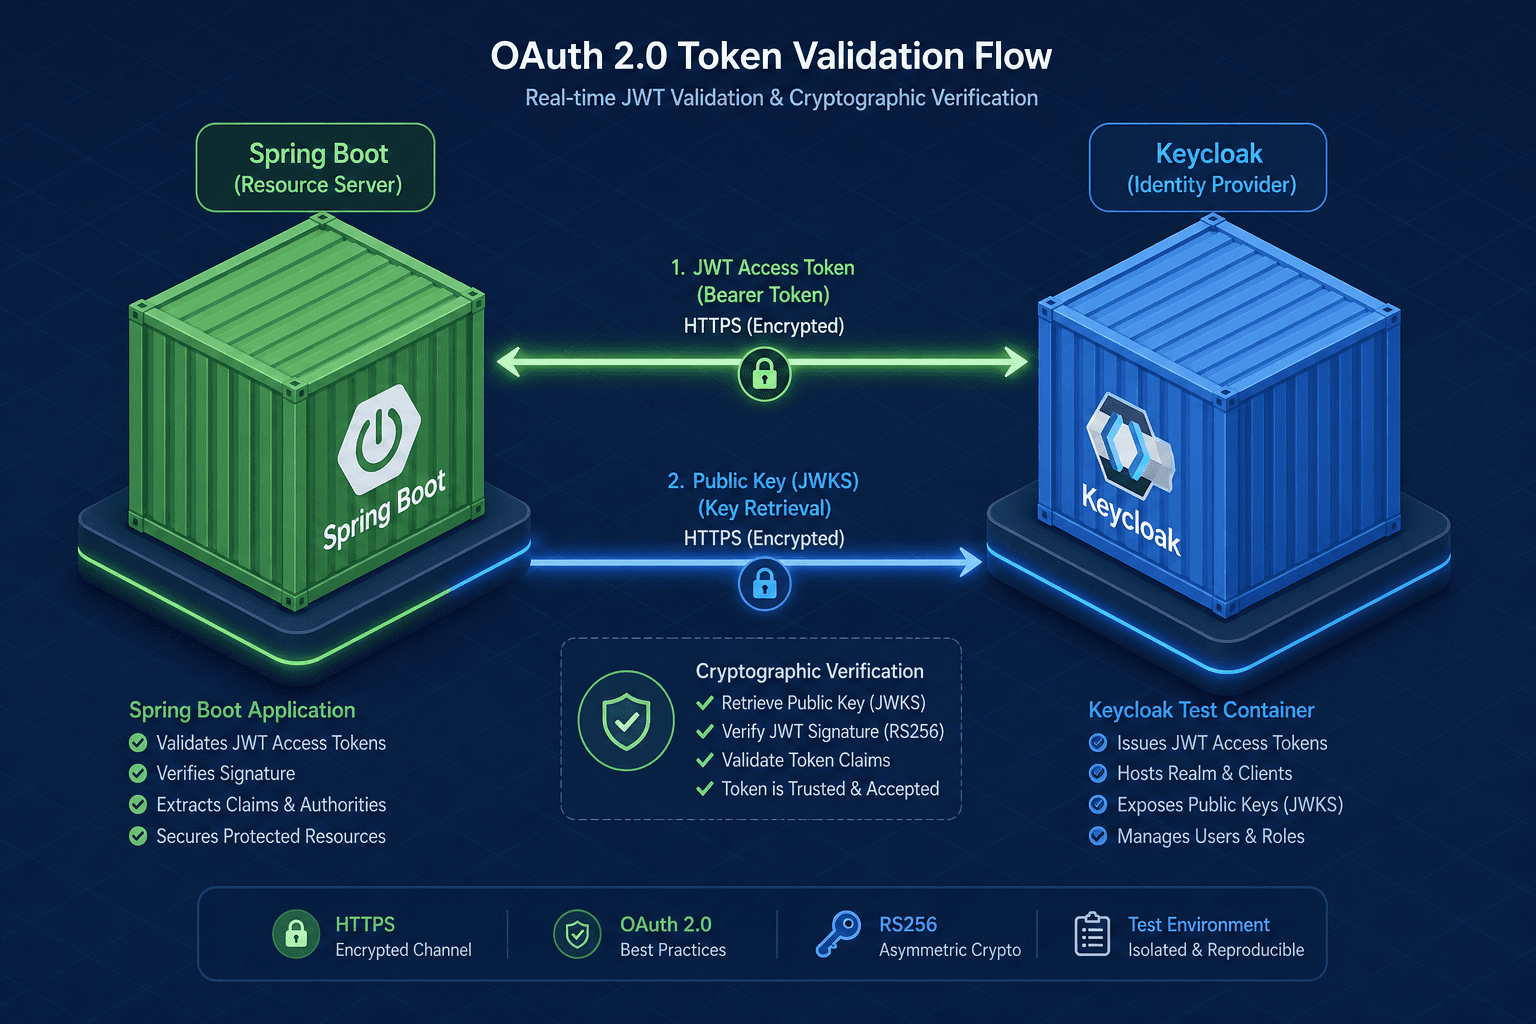
Learn how to effectively test OAuth 2.0 integrations with Spring Boot and Keycloak test containers in this technical walkthrough for developers.
Part 10 · OAuth 2.0 Deep Dive SeriesTag
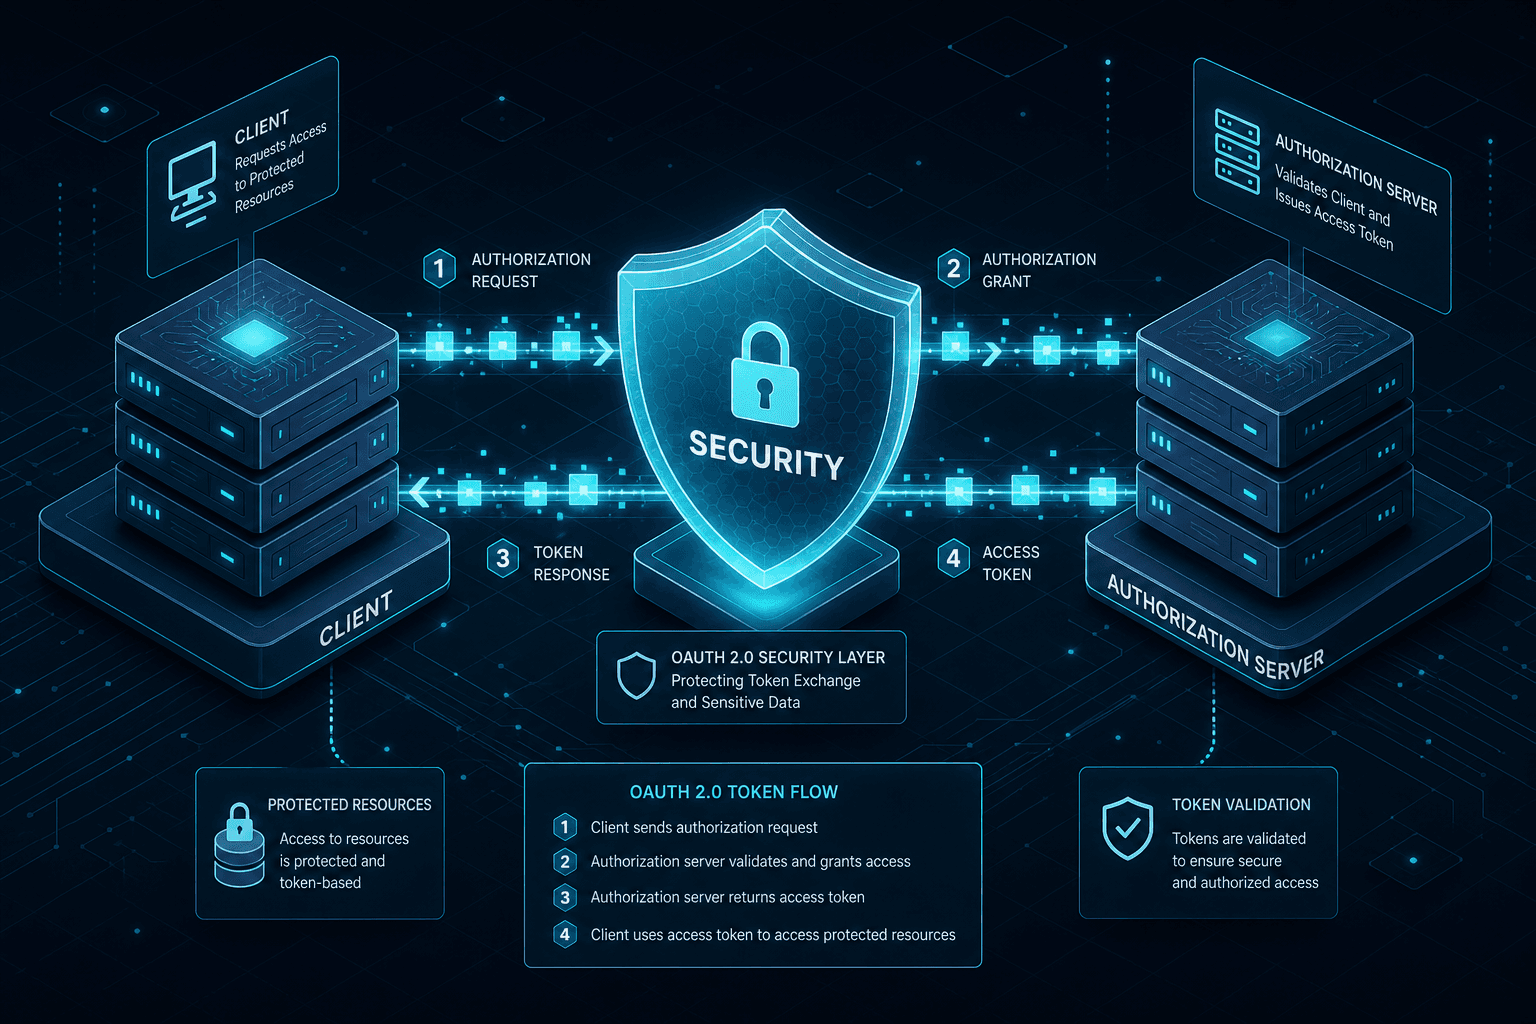
Authentication patterns and protocols — OAuth 2.0, OIDC, SAML, MFA, passwordless, and session strategies for modern applications.
144 posts · page 8 of 8
Learn how to effectively test OAuth 2.0 integrations with Spring Boot and Keycloak test containers in this technical walkthrough for developers.
Part 10 · OAuth 2.0 Deep Dive SeriesLearn how to secure OAuth 2.0 implementations by preventing common vulnerabilities such as CSRF attacks and token leakage through proven hardening techniques.
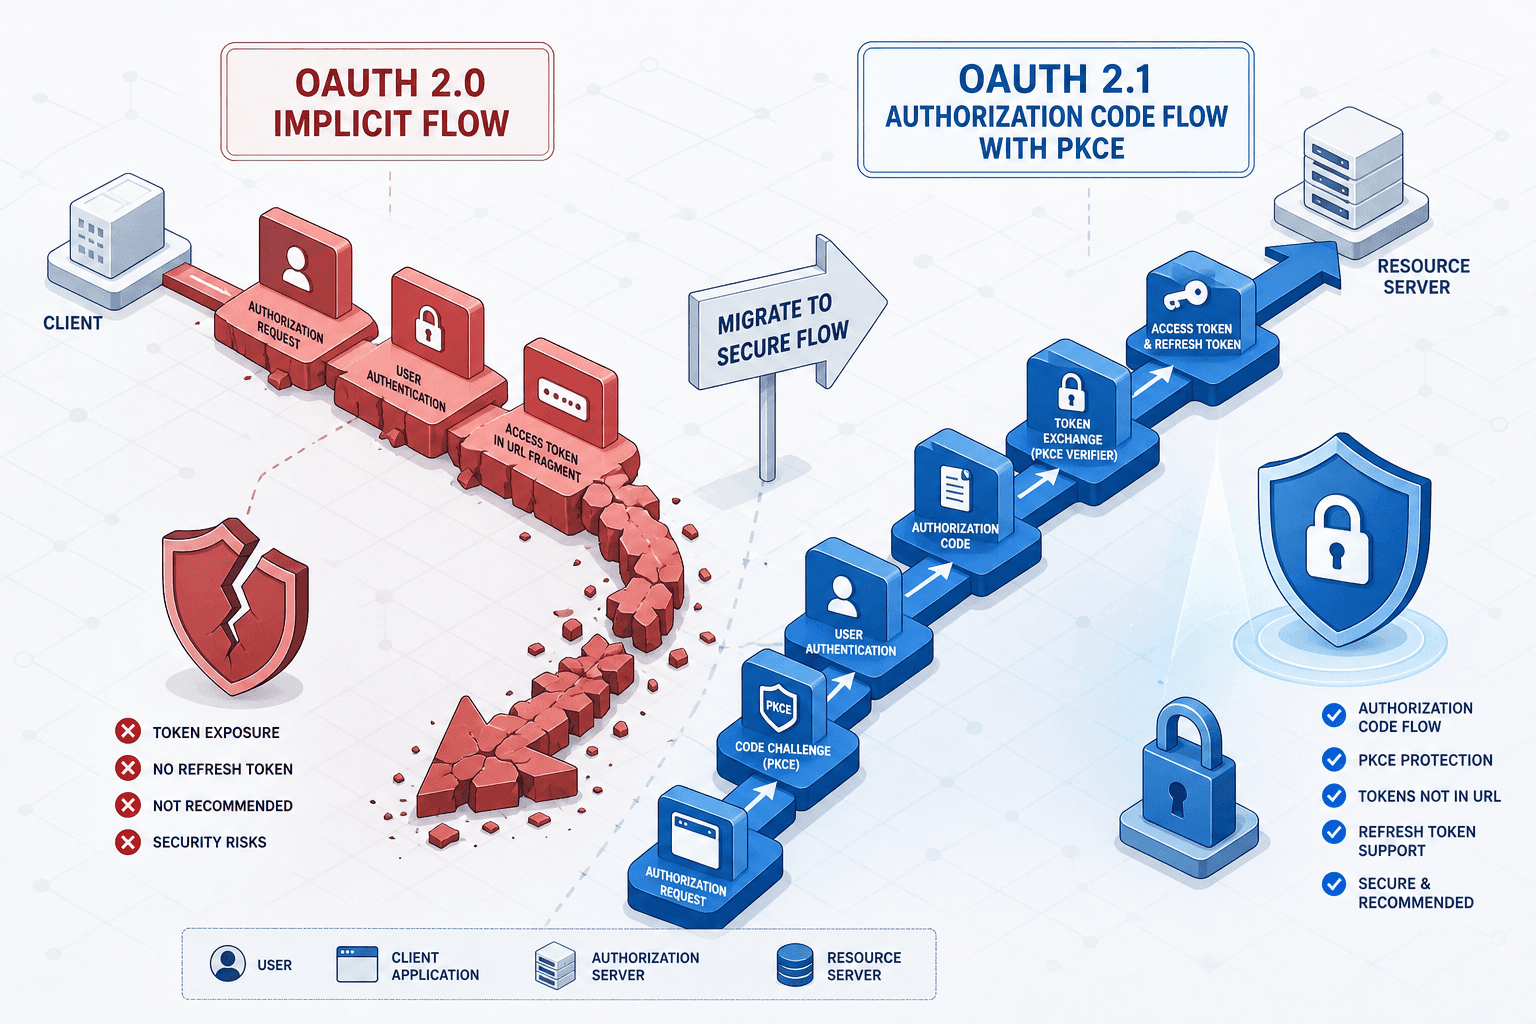
Part 9 · OAuth 2.0 Deep Dive SeriesLearn how to prepare for OAuth 2.1 with mandatory PKCE, key deprecations, and essential security updates for a secure transition.
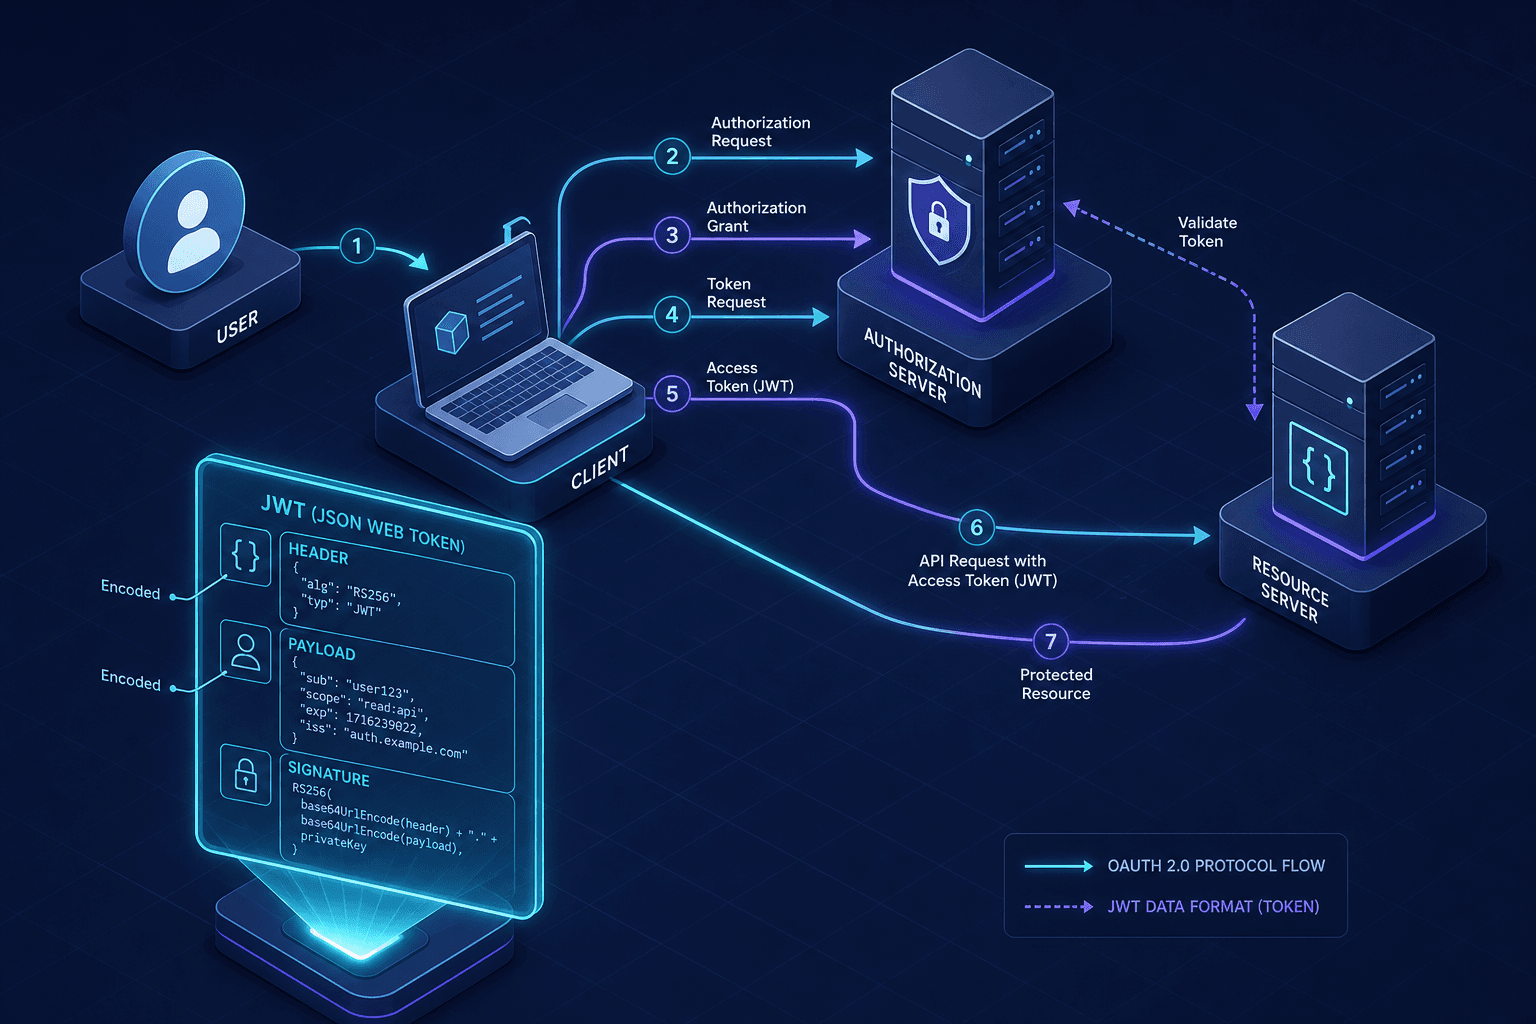
Part 7 · OAuth 2.0 Deep Dive SeriesClarify how OAuth 2.0 protocols interact with JSON Web Tokens. Learn about opaque tokens, format selection strategies, and essential best practices for secure implementation.
Part 6 · OAuth 2.0 Deep Dive Series