6 min readBackendFeatured
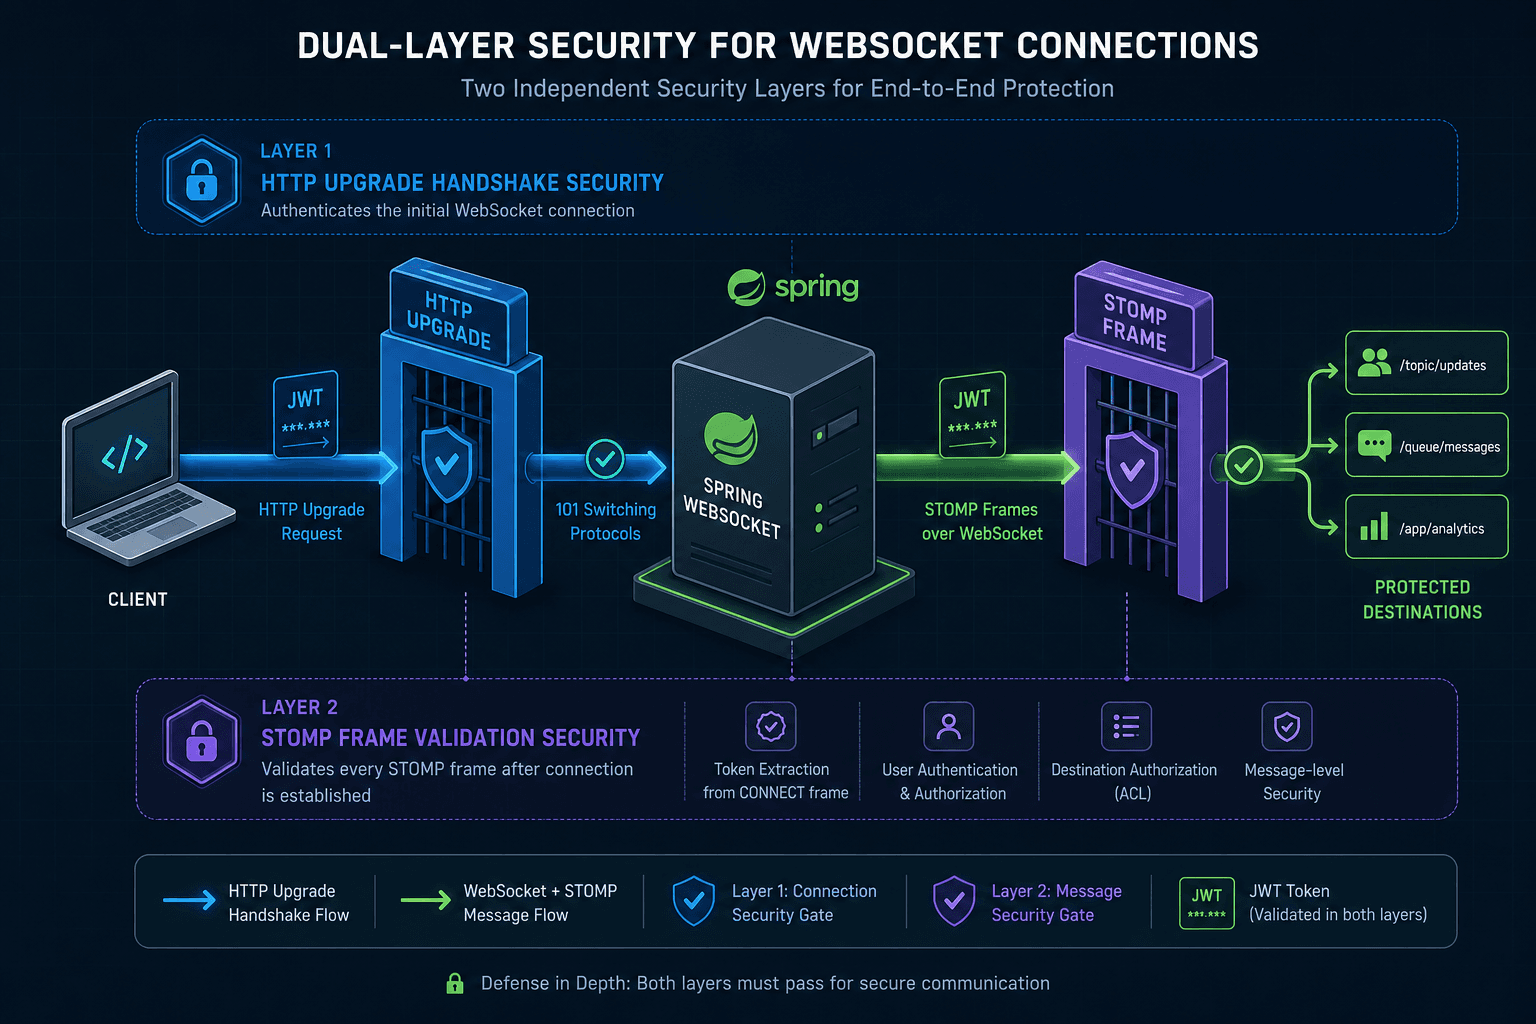
Securing WebSocket Connections with OAuth2 and JWT
Learn how to implement secure real-time applications by integrating OAuth2 and JWT with Spring WebSocket and STOMP protocols.
Tag
JWT structure, signing, validation, expiration, rotation, and revocation strategies — everything a backend engineer needs to ship safely.
25 posts · page 2 of 2
Learn how to implement secure real-time applications by integrating OAuth2 and JWT with Spring WebSocket and STOMP protocols.
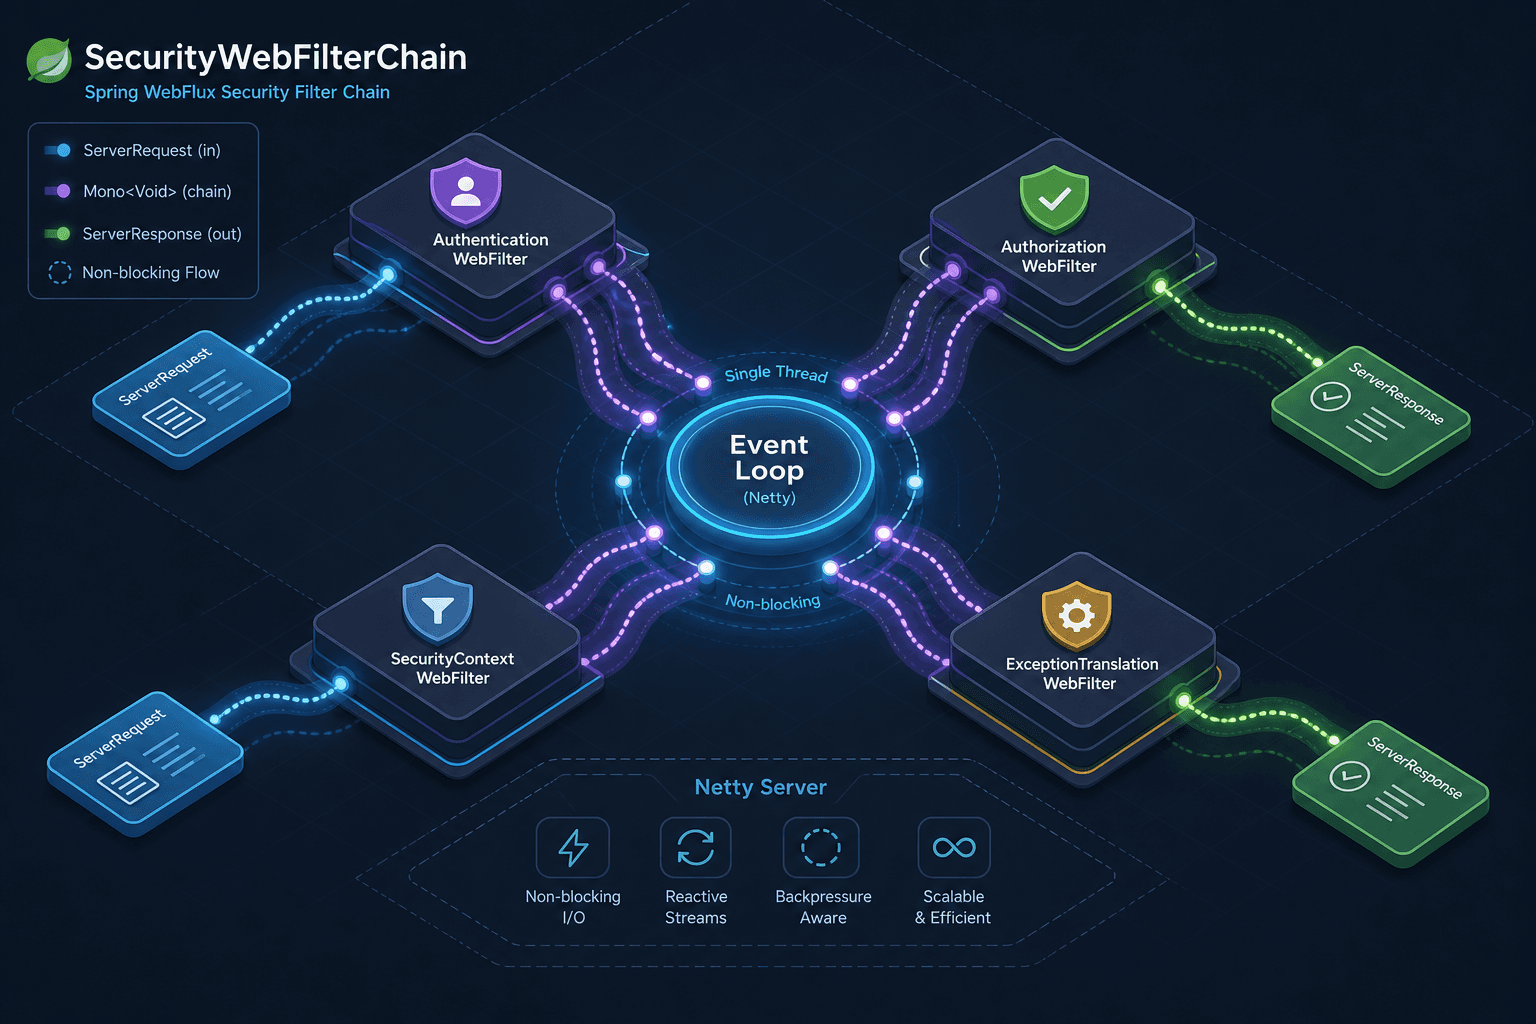
Learn how to implement security patterns in reactive Spring applications using WebFlux, including reactive JWT and authentication flows.
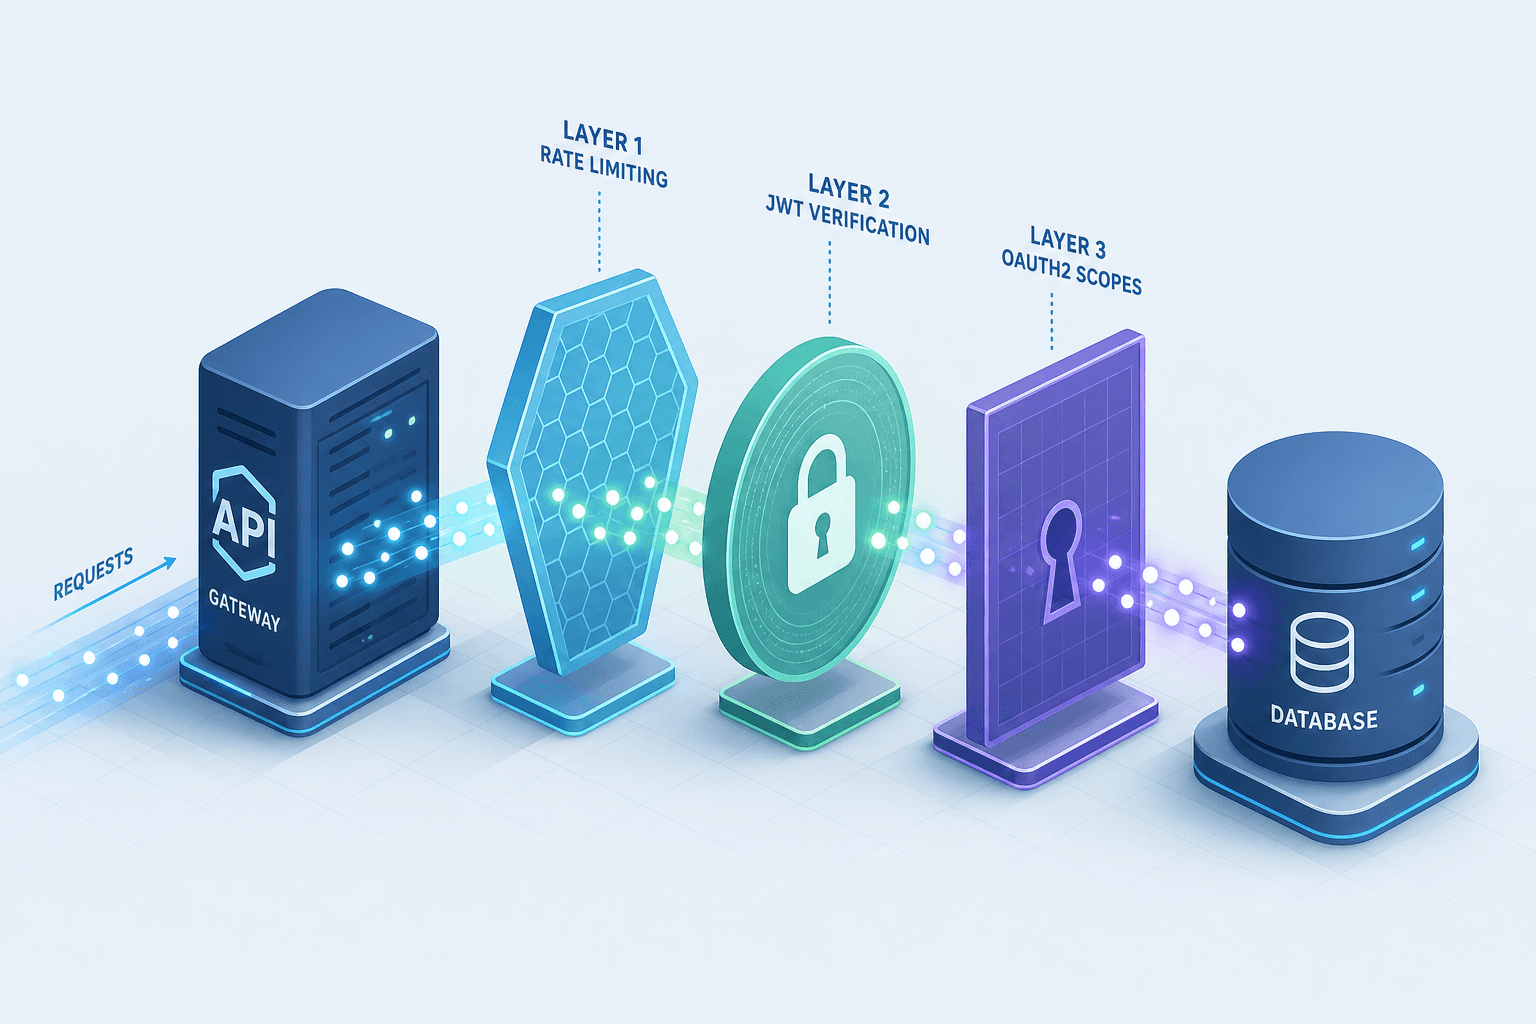
Part 7 · Spring Security Deep Dive SeriesLearn how to secure your APIs using rate limiting, JSON Web Tokens, and proper OAuth2 scope management to prevent unauthorized access.
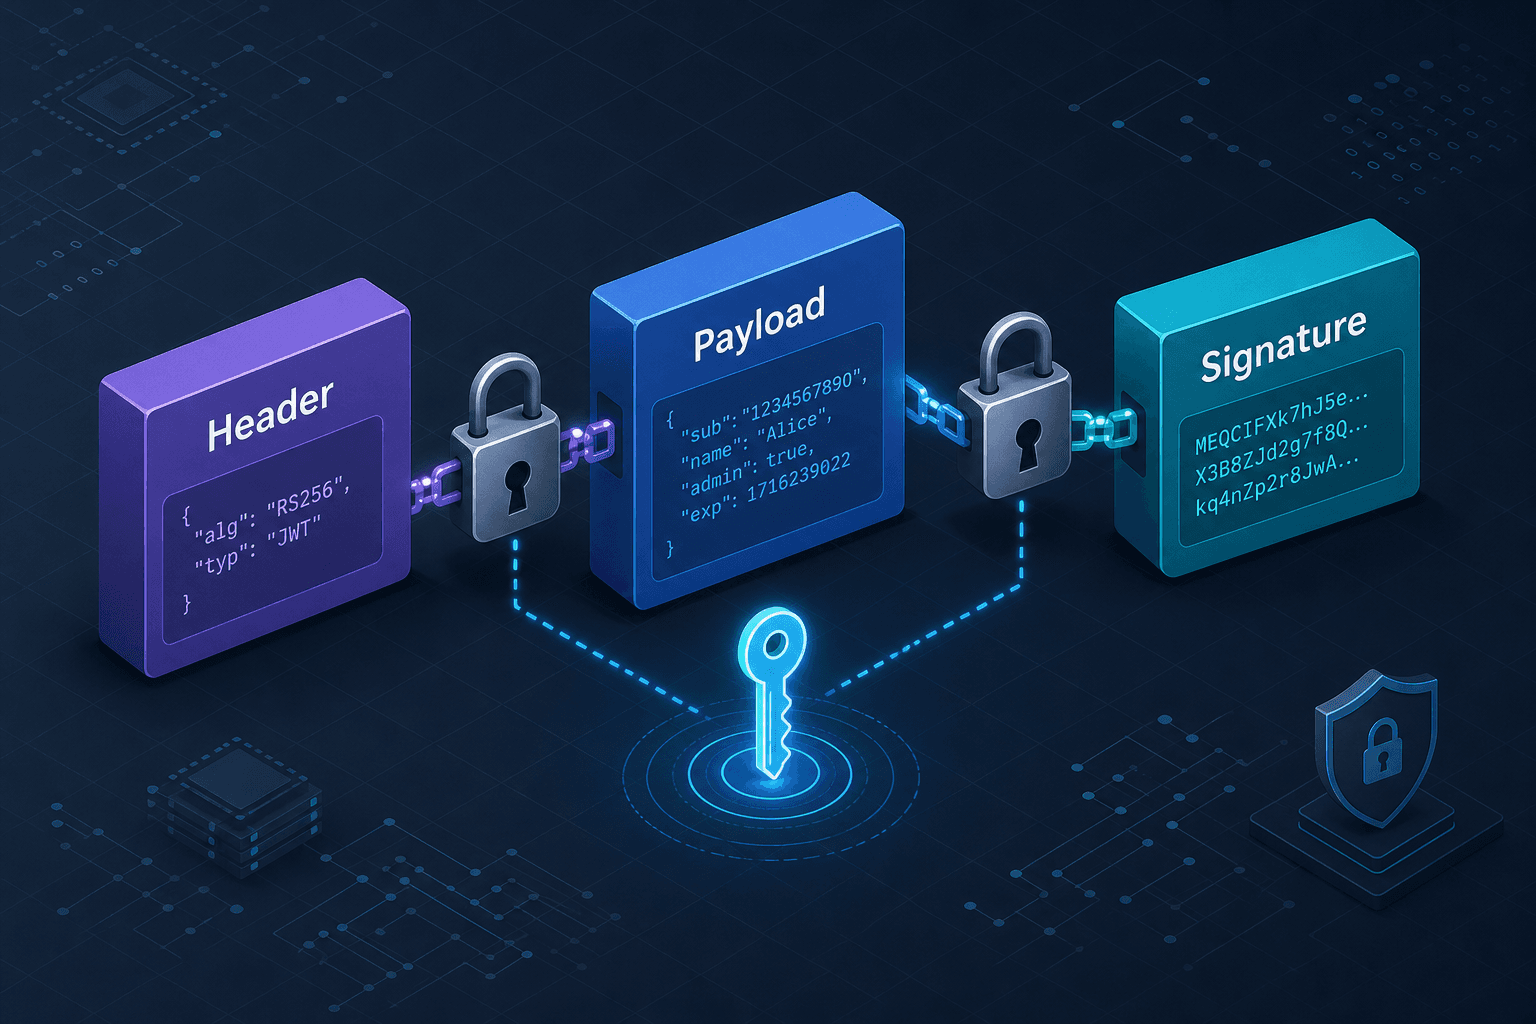
Part 6 · Zero Trust & Modern Security Architecture SeriesExplore the core components of JSON Web Tokens, including JWS and JWE, and learn how to properly sign and validate them for secure applications.
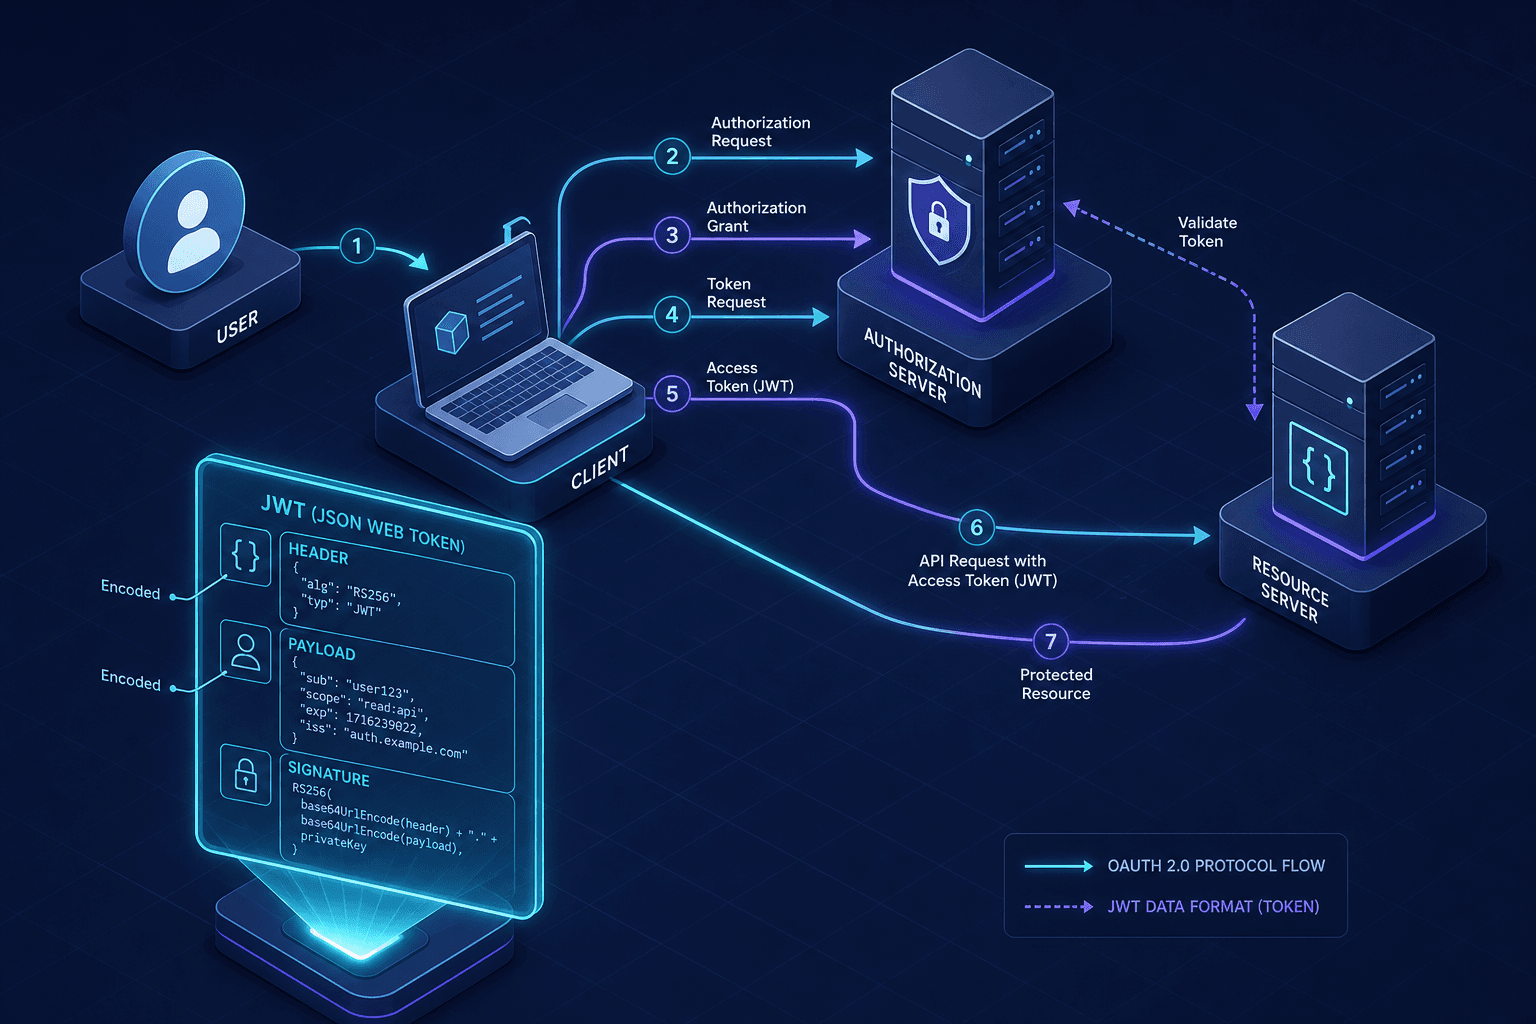
Part 2 · OpenID Connect Deep Dive SeriesClarify how OAuth 2.0 protocols interact with JSON Web Tokens. Learn about opaque tokens, format selection strategies, and essential best practices for secure implementation.
Part 6 · OAuth 2.0 Deep Dive Series