Multi-Factor Authentication with OIDC: Implementing MFA
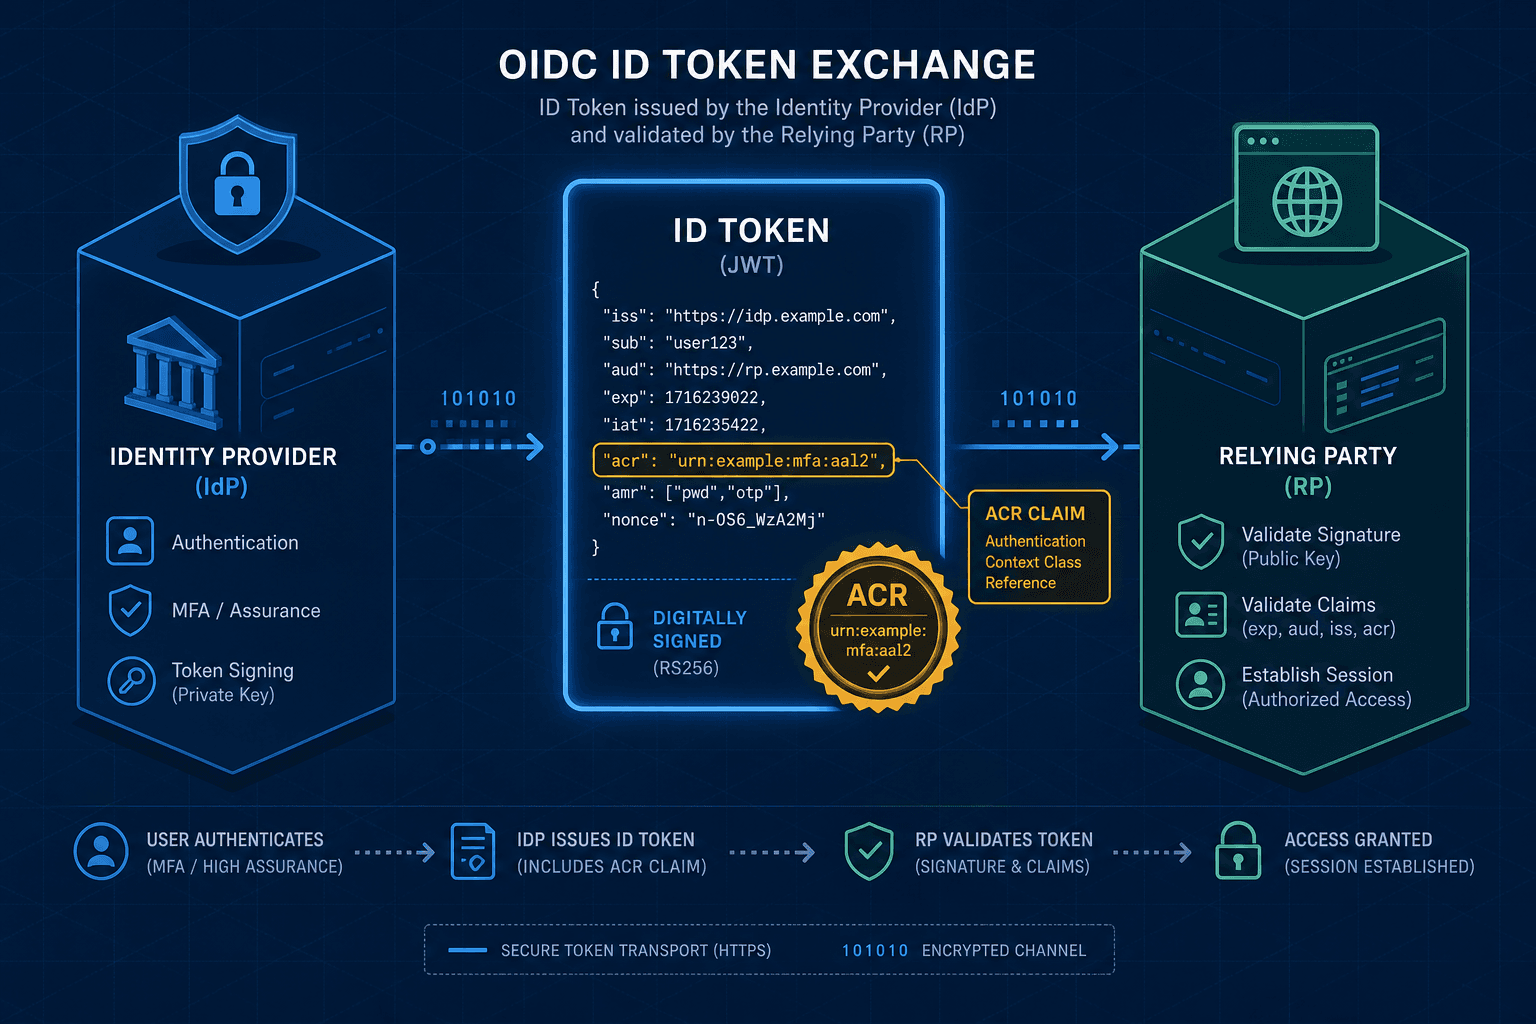
Learn to secure OIDC flows with effective multi-factor authentication strategies including WebAuthn, TOTP, and dynamic step-up challenges using ACR.
Part 7 · OpenID Connect Deep Dive SeriesBlog
Practical guides on OAuth 2.0, OpenID Connect, SAML, Keycloak, and the platform engineering behind identity systems.
595 posts · page 19 of 30
Learn to secure OIDC flows with effective multi-factor authentication strategies including WebAuthn, TOTP, and dynamic step-up challenges using ACR.
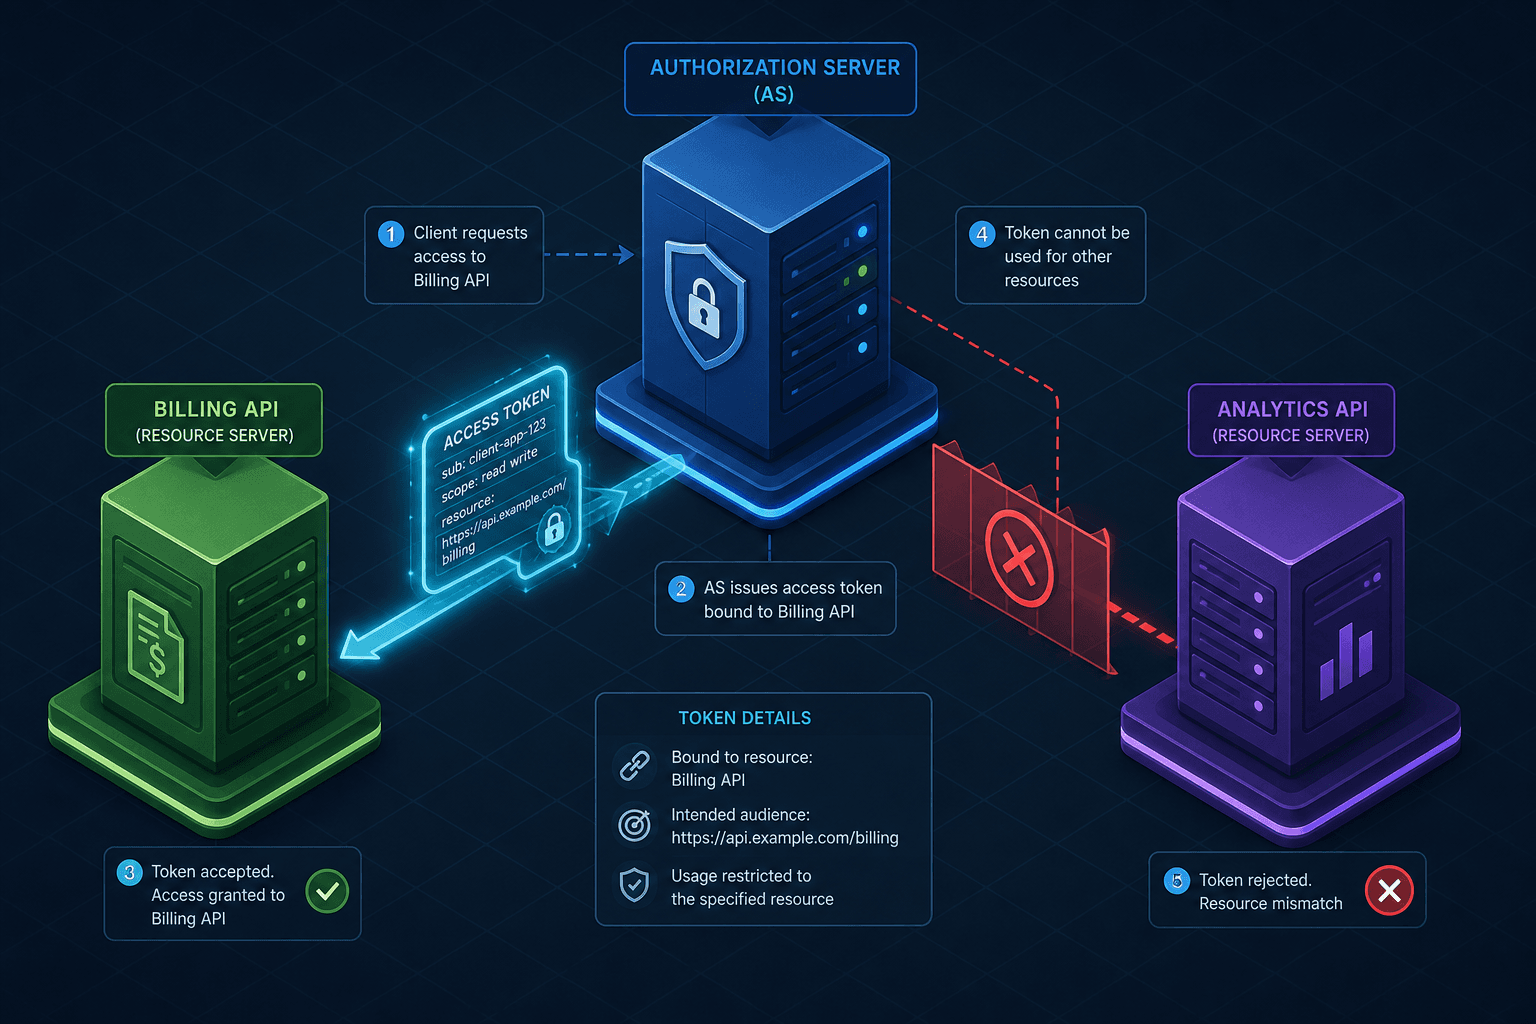
Part 7 · OpenID Connect Deep Dive SeriesLearn how to apply RFC 8707 resource indicators for precise audience restrictions and secure multi-resource access patterns in OAuth2 flows.
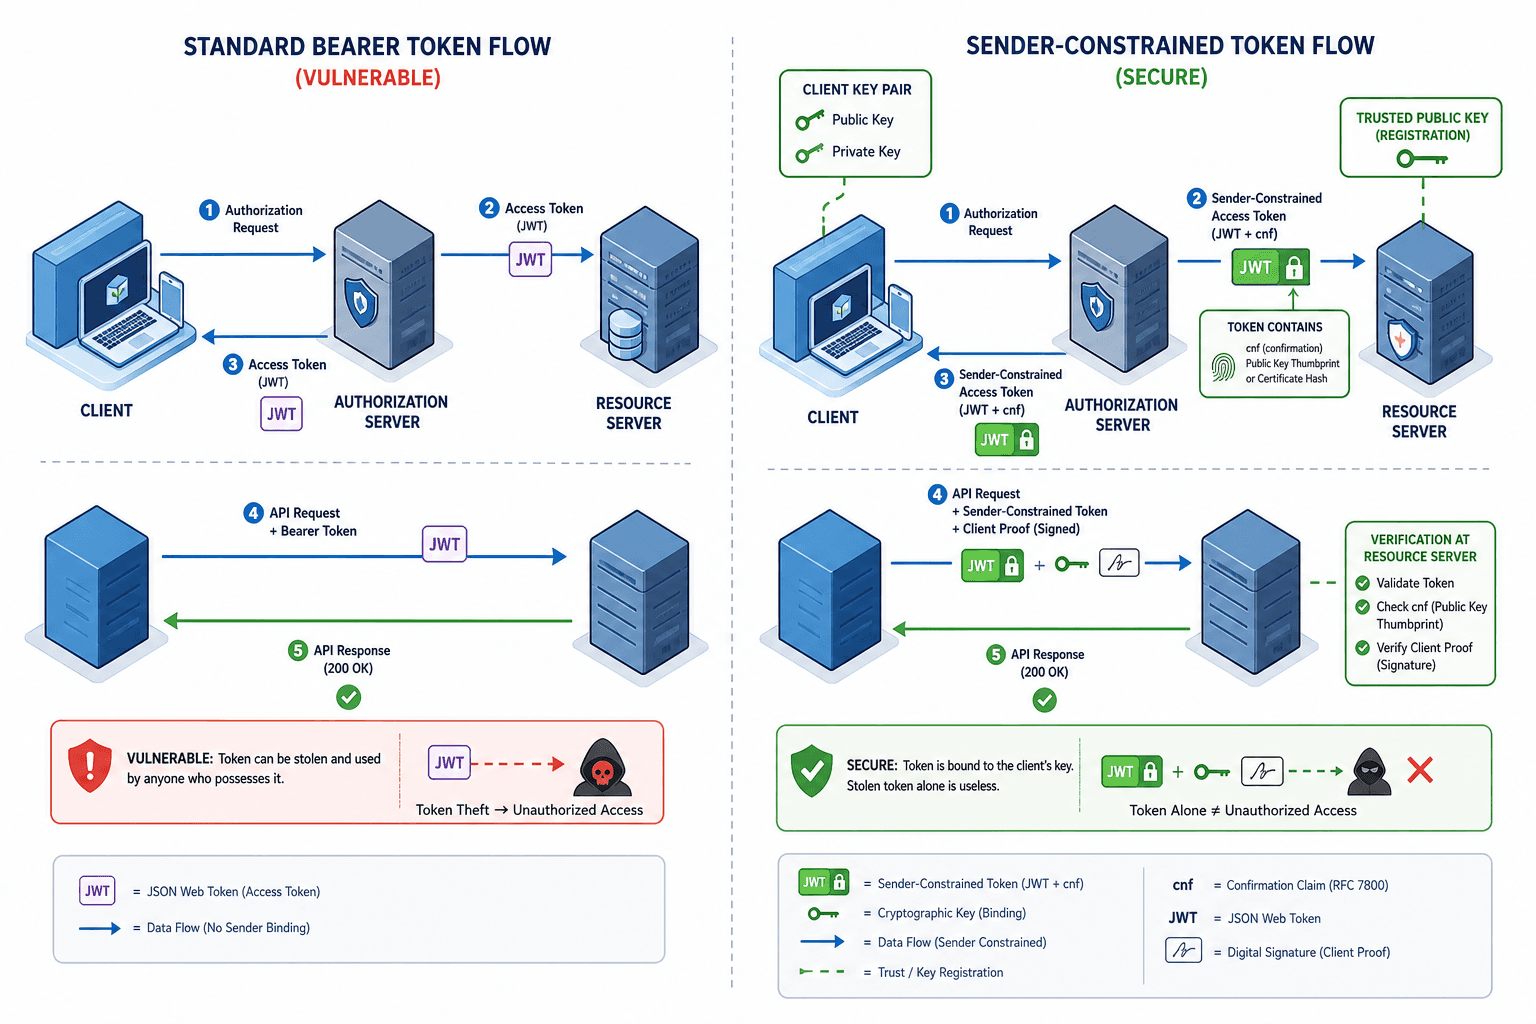
Part 6 · OAuth 2.0 SecurityLearn how sender-constrained tokens like DPoP and mTLS strengthen security by binding tokens to specific clients and preventing misuse.
Part 5 · OAuth 2.0 SecurityUnderstand the core OAuth 2.0 grant types like authorization code, client credentials, and PKCE to implement secure authentication flows effectively.
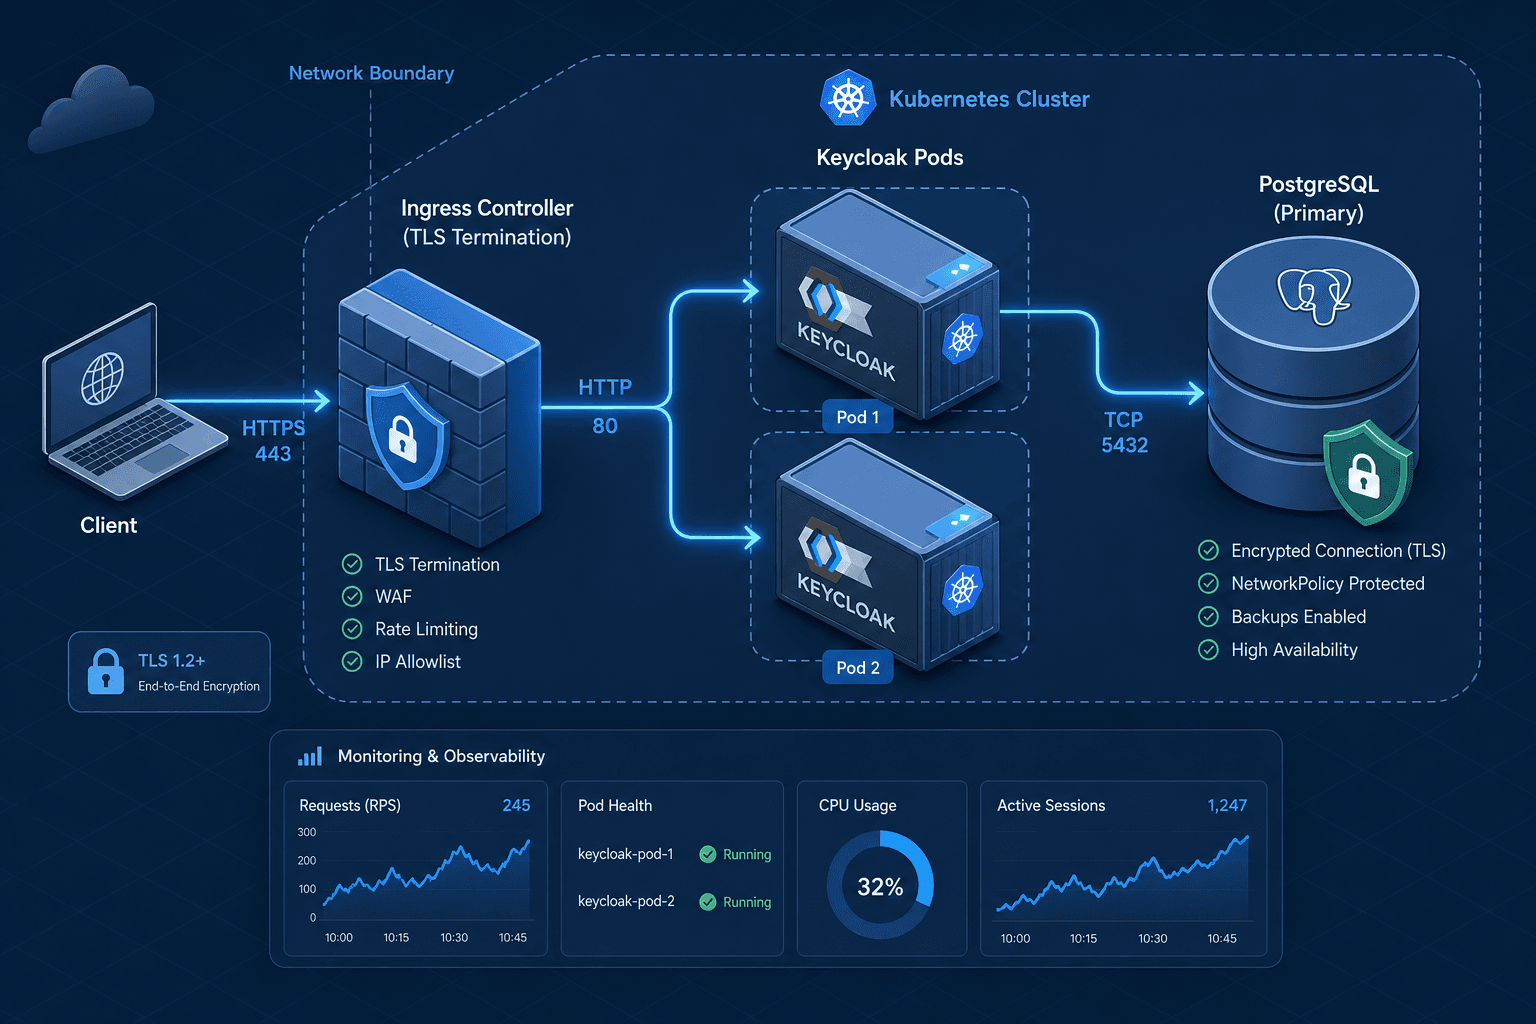
Part 1 · OAuth 2.0 Deep Dive SeriesLearn how to deploy Keycloak securely in production using Docker and Kubernetes, including SSL configuration and monitoring strategies.
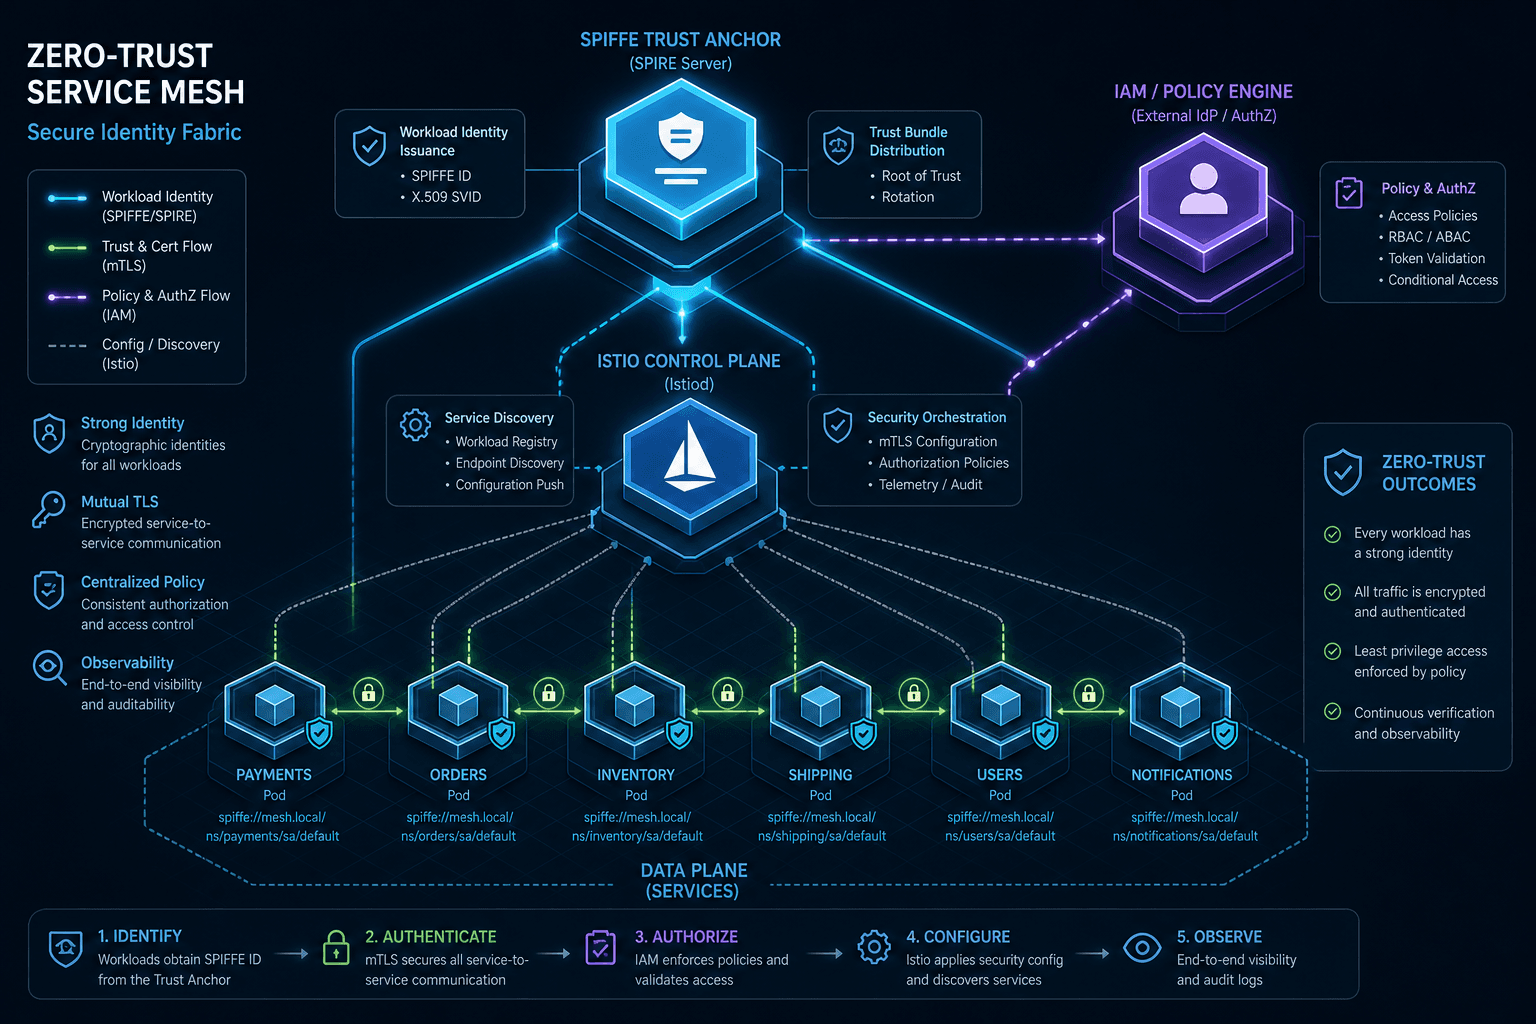
Part 2 · Keycloak Masterclass SeriesLearn how to integrate IAM with service mesh architectures to enforce strong identity policies between services using SPIFFE and Istio.
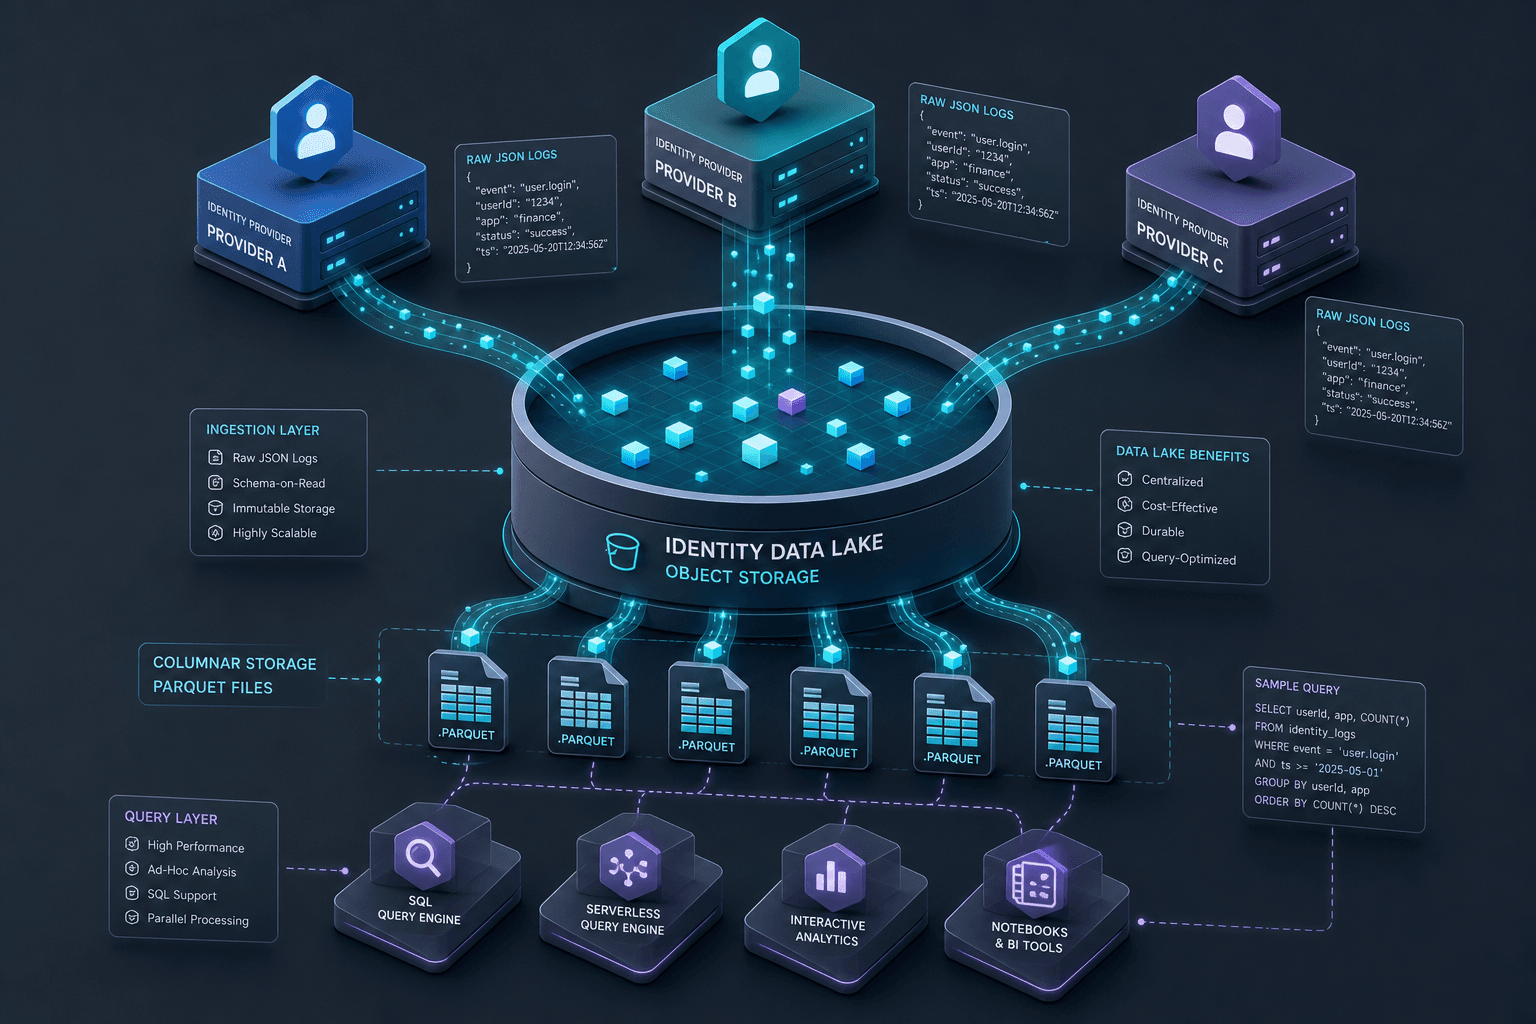
Part 5 · Identity Gateways & Legacy IntegrationLearn how to construct an identity data lake designed for effective analytics on access patterns, supporting security data lakes, identity analytics, and compliance reporting needs.
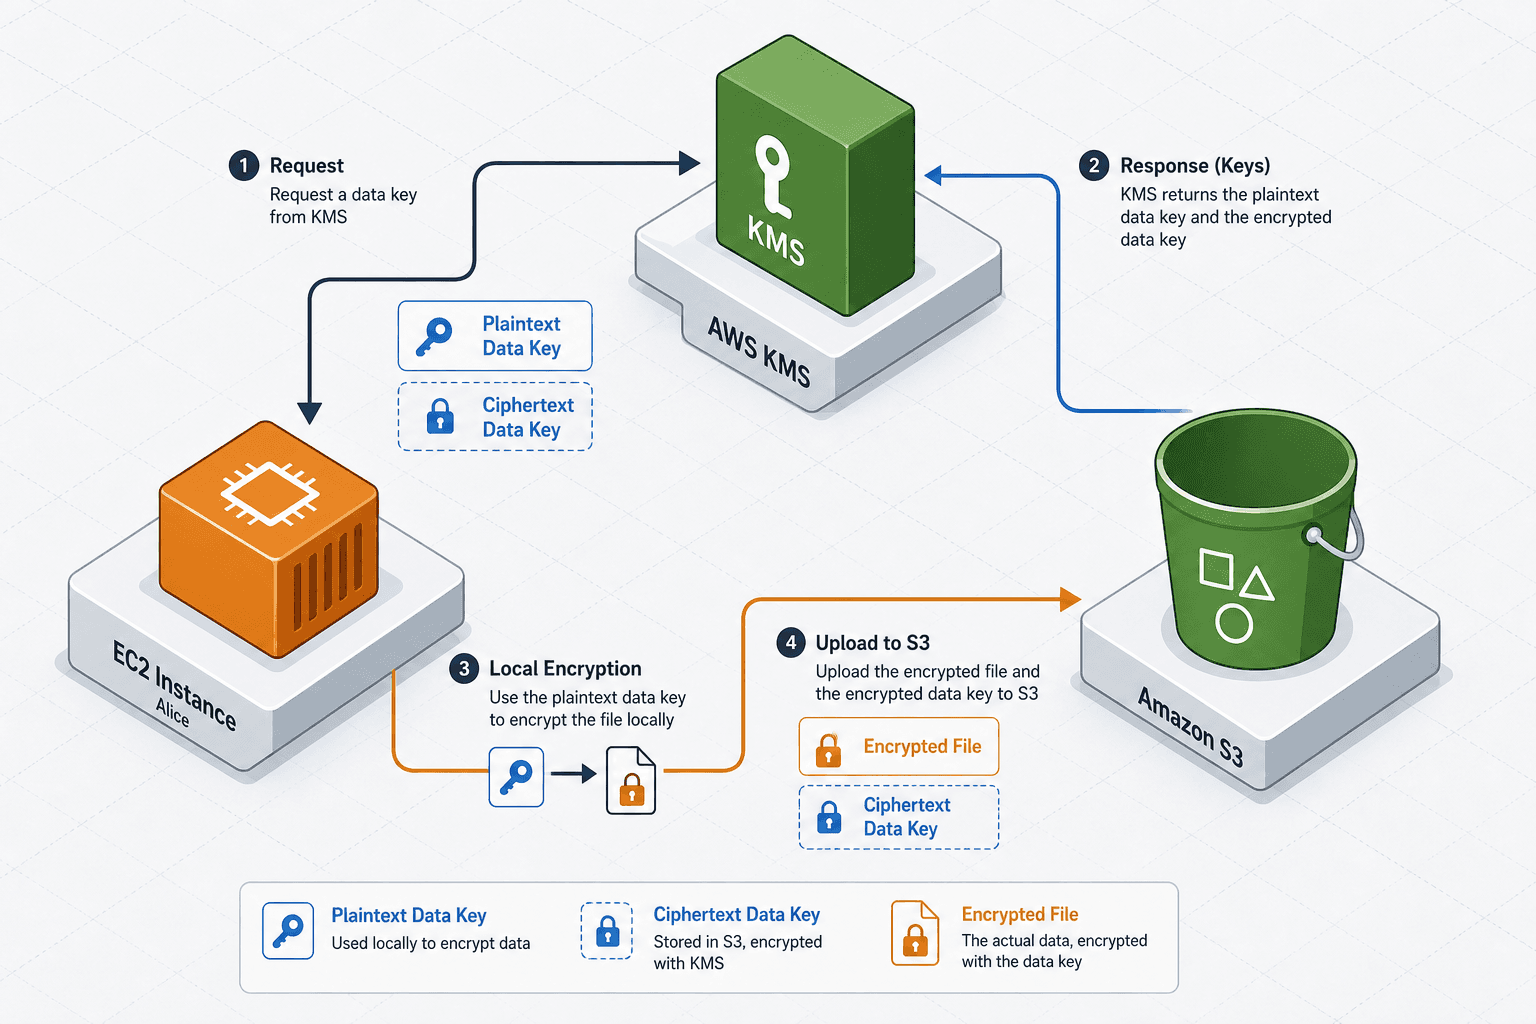
Part 5 · Identity Analytics & ObservabilityA technical overview of AWS Key Management Service, covering Customer Master Keys, data key generation, and the envelope encryption pattern for secure cloud storage.
Part 2 · AWS Secrets and Key ManagementChoosing between AWS Secrets Manager and SSM Parameter Store can be tricky. This guide breaks down the differences in cost, automatic rotation, and security to help you make the right choice.
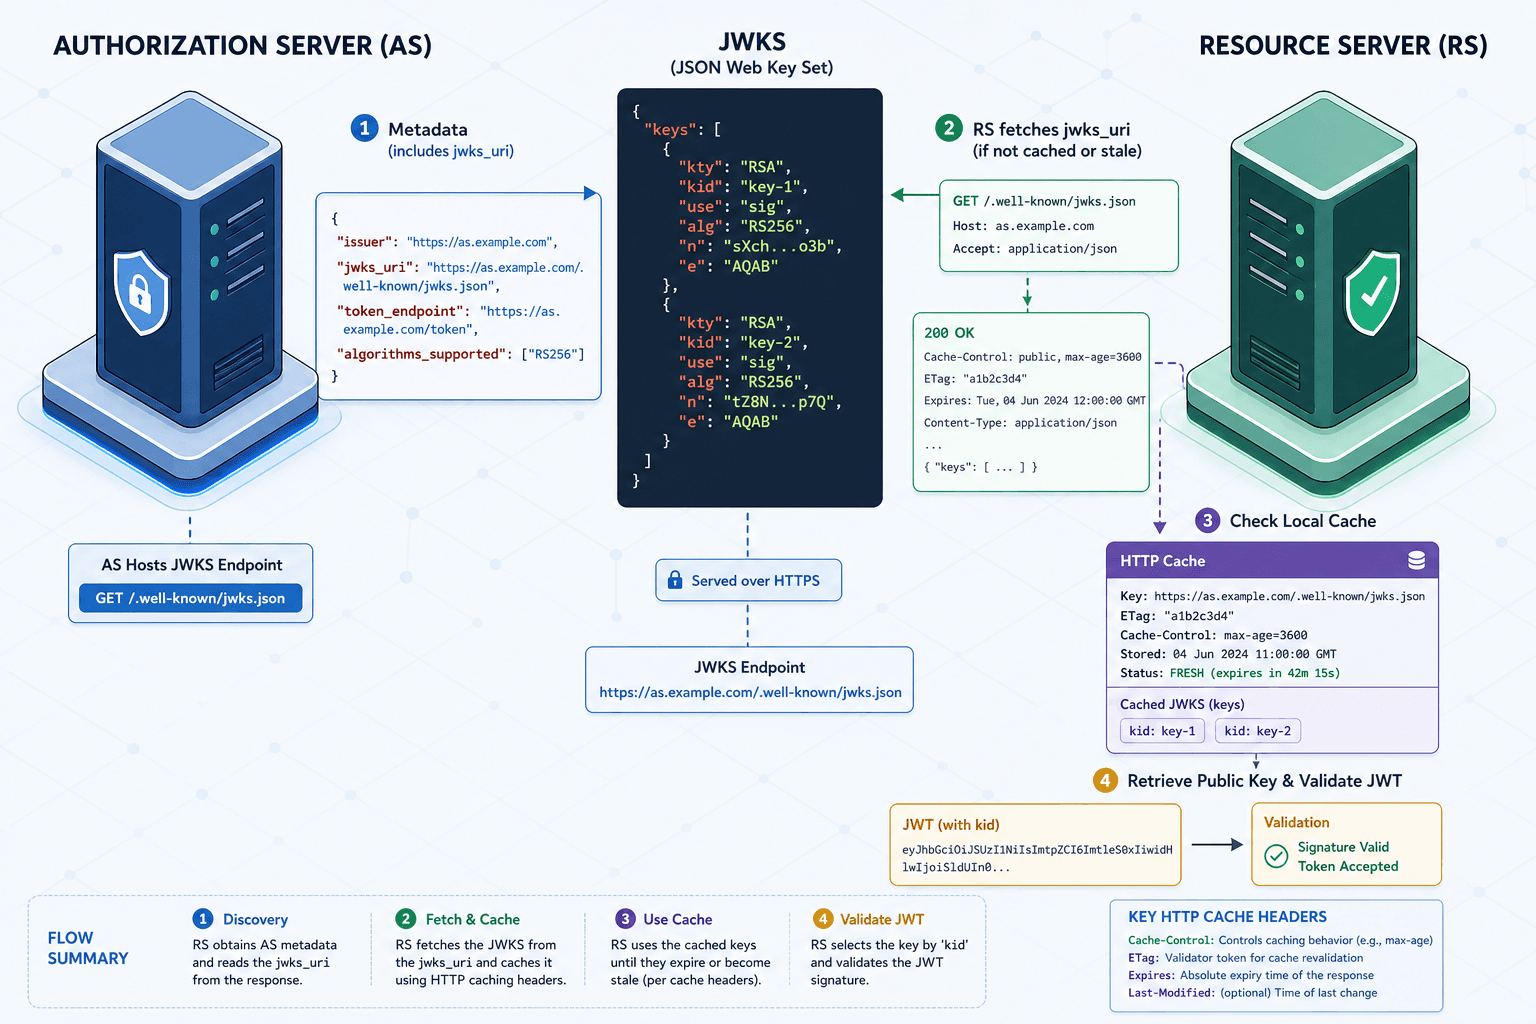
Part 1 · AWS Secrets and Key ManagementLearn how to implement secure key discovery using JWKS URI, manage key rotation, and optimize caching strategies in line with RFC 8414.
Part 3 · Authorization Server Metadata (RFC 8414)A guide to configuring OAuth2/OIDC in standalone Angular apps using provideOAuthClient, replacing traditional NgModule providers.
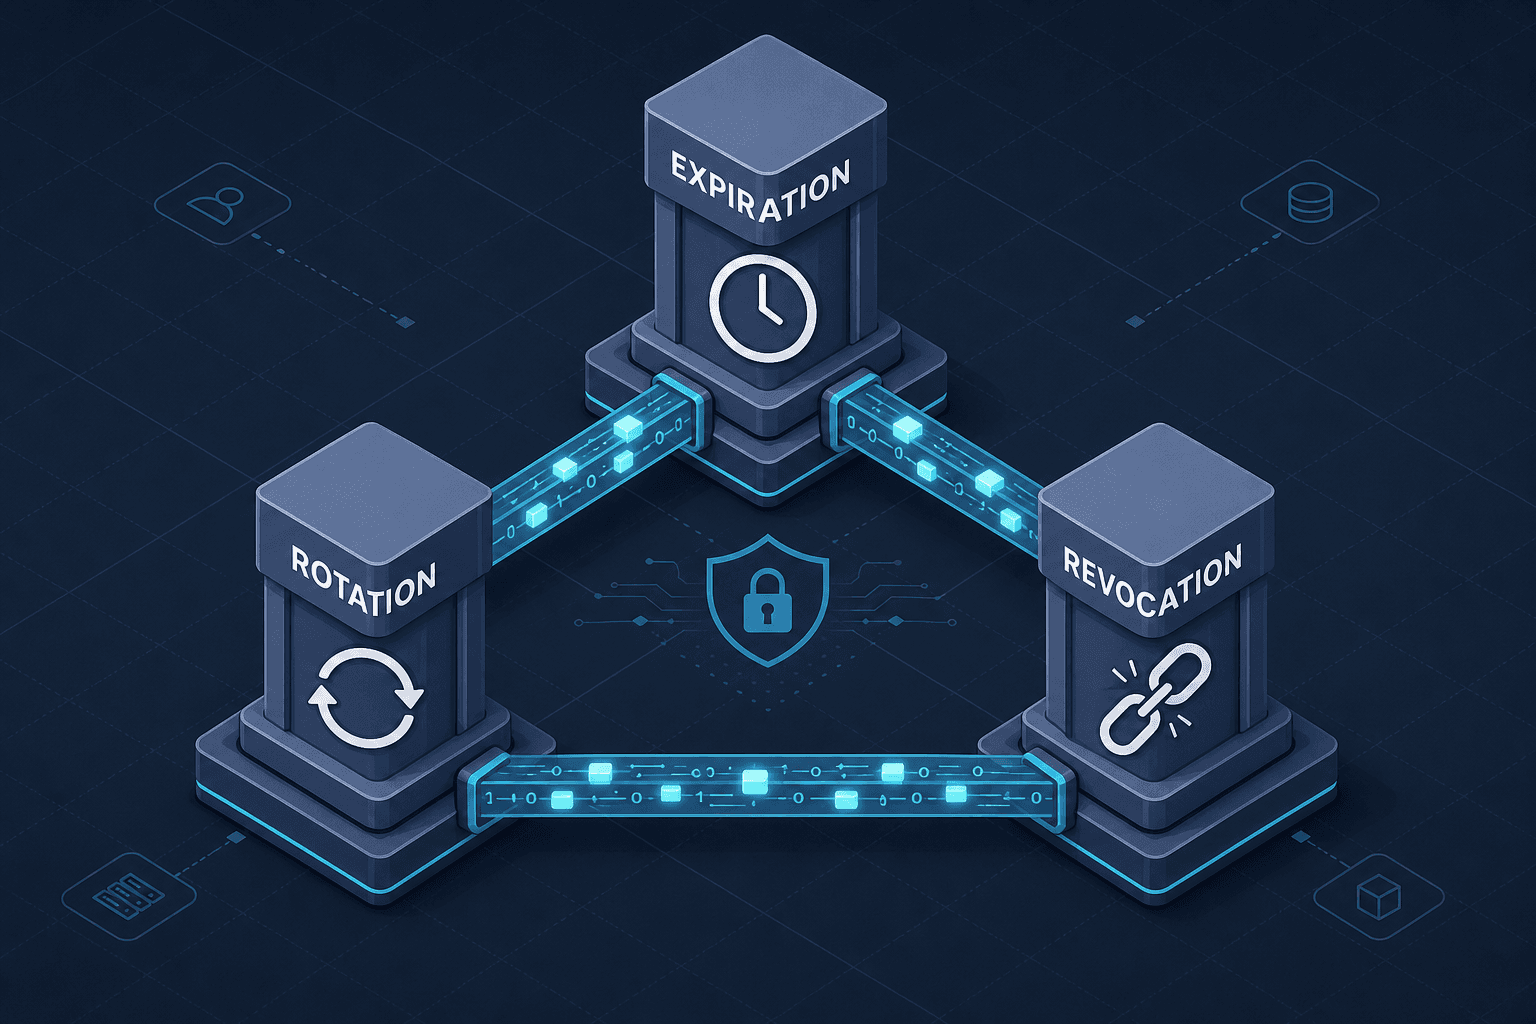
Part 8 · angular-oauth2-oidc in ProductionLearn how to manage JWT expiration, rotation, and revocation effectively to secure your application's token lifecycle.
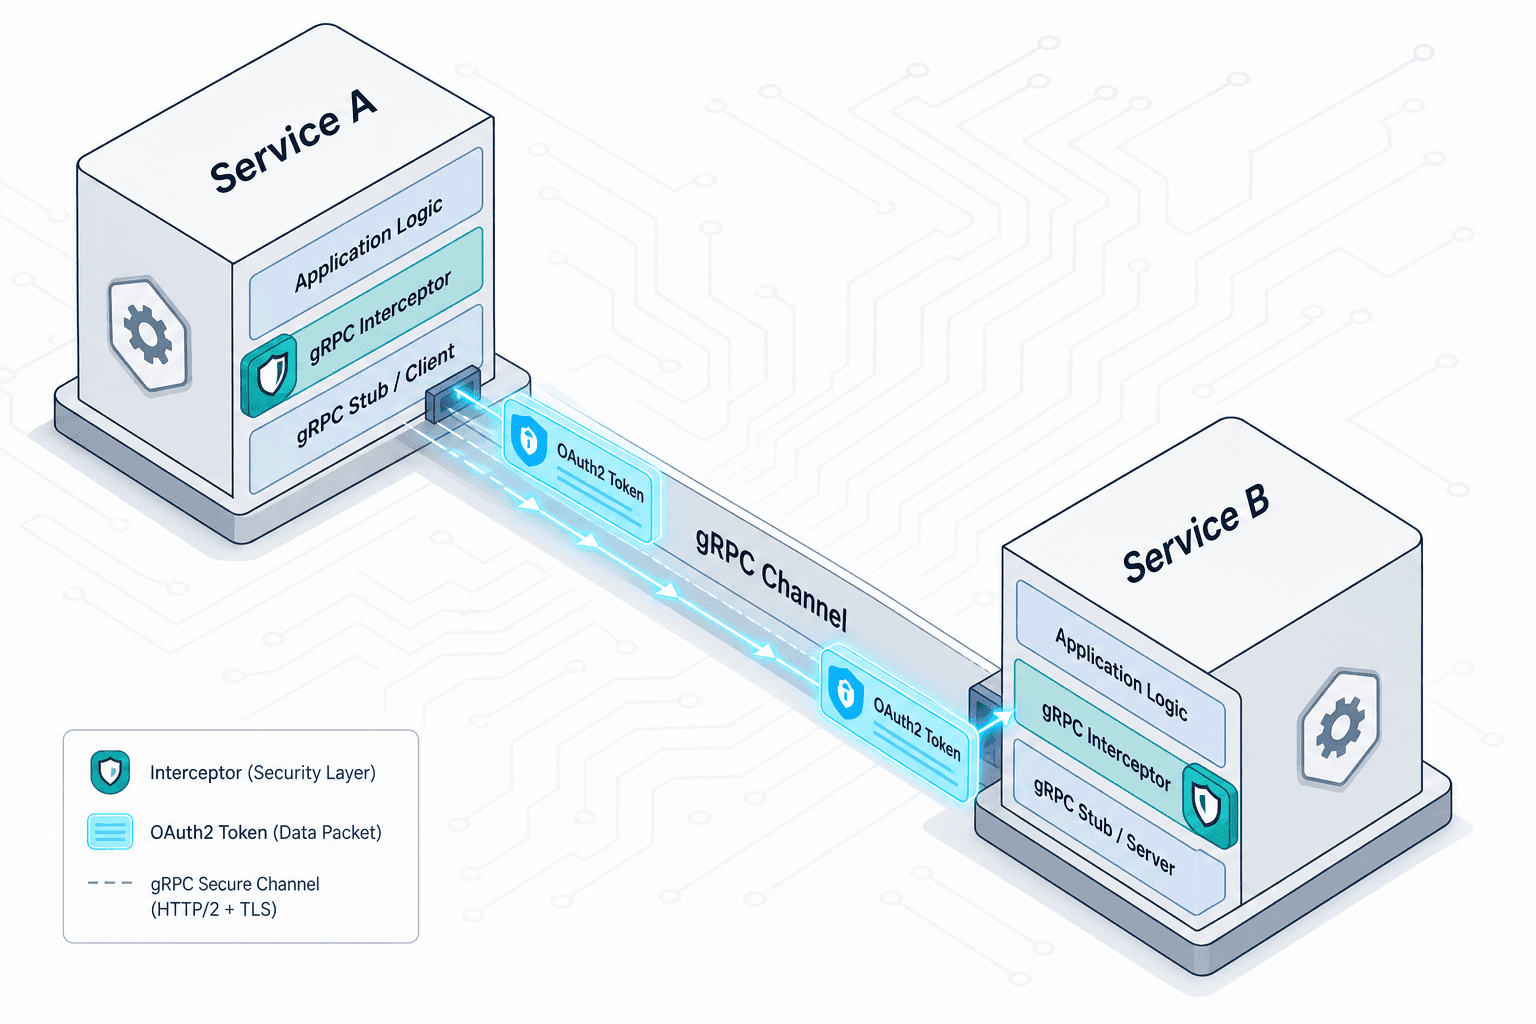
Learn how to implement gRPC interceptors to propagate OAuth2 tokens securely across microservices for improved service-to-service security.
Your IAM system is compromised. Learn the critical steps for identity breach response, including incident handling and securing compromised credentials.
Zero Trust is more than a buzzword. This guide breaks down the actual technical requirements, NIST tenets, and maturity models needed for implementation.
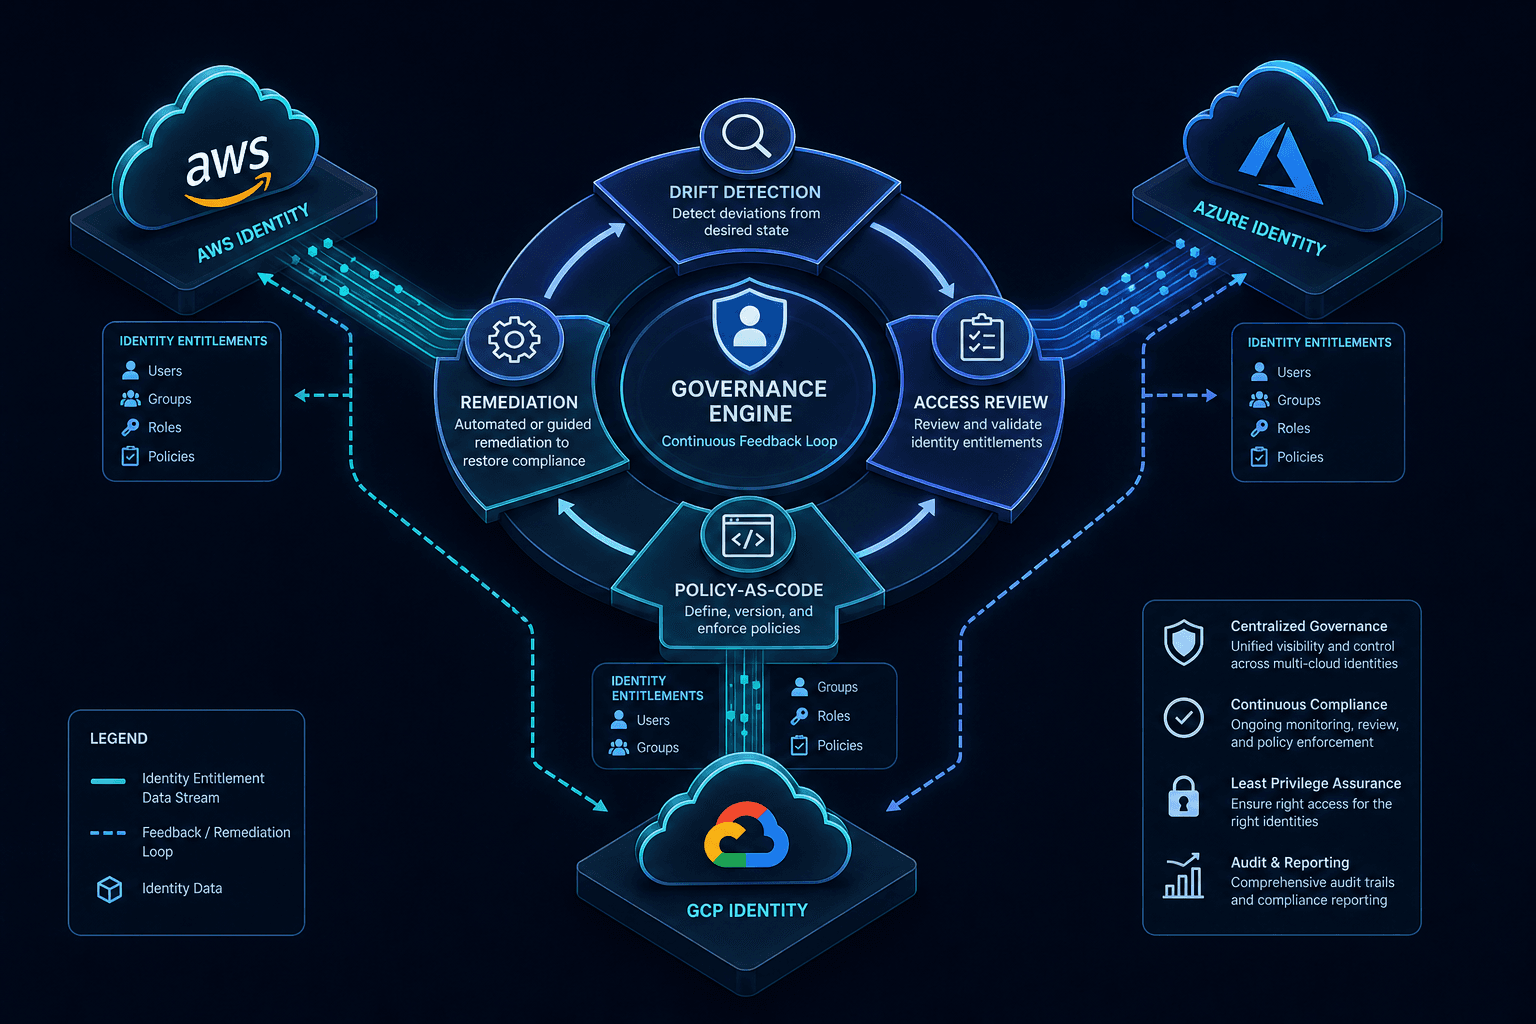
Part 1 · Zero Trust, ImplementedA technical look at managing access reviews and identifying entitlement drift in multi-cloud identity governance frameworks.
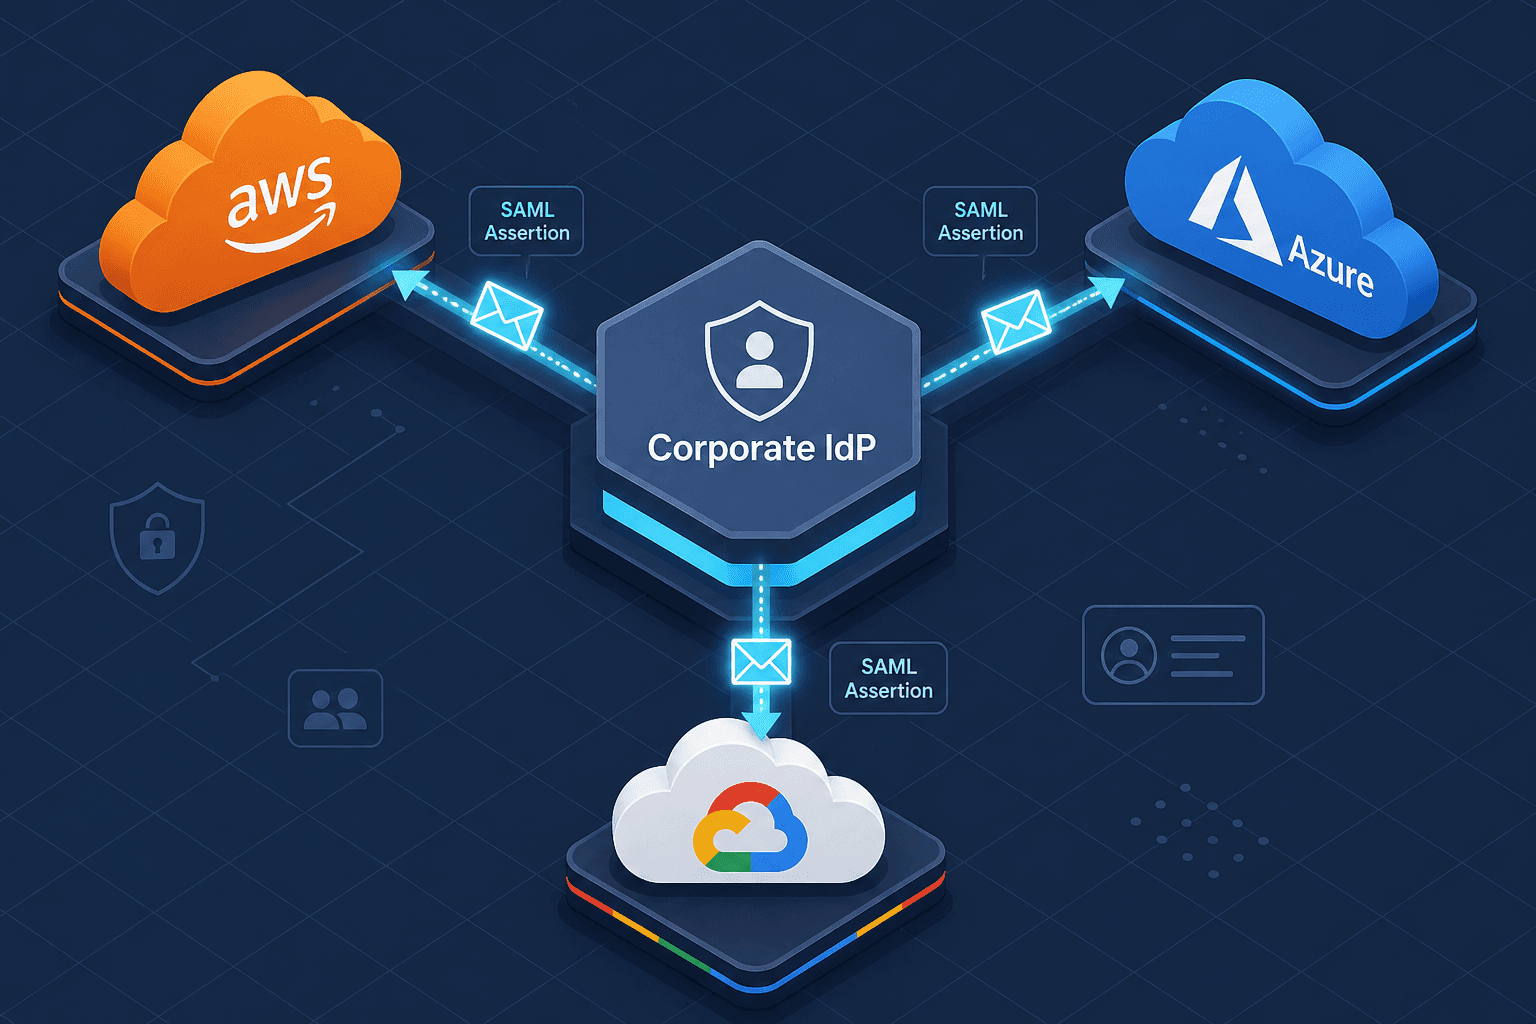
Part 6 · Multi-Cloud IdentityA technical walkthrough for cloud and identity engineers on unifying AWS, Azure, and GCP access through a single SAML-based identity provider.
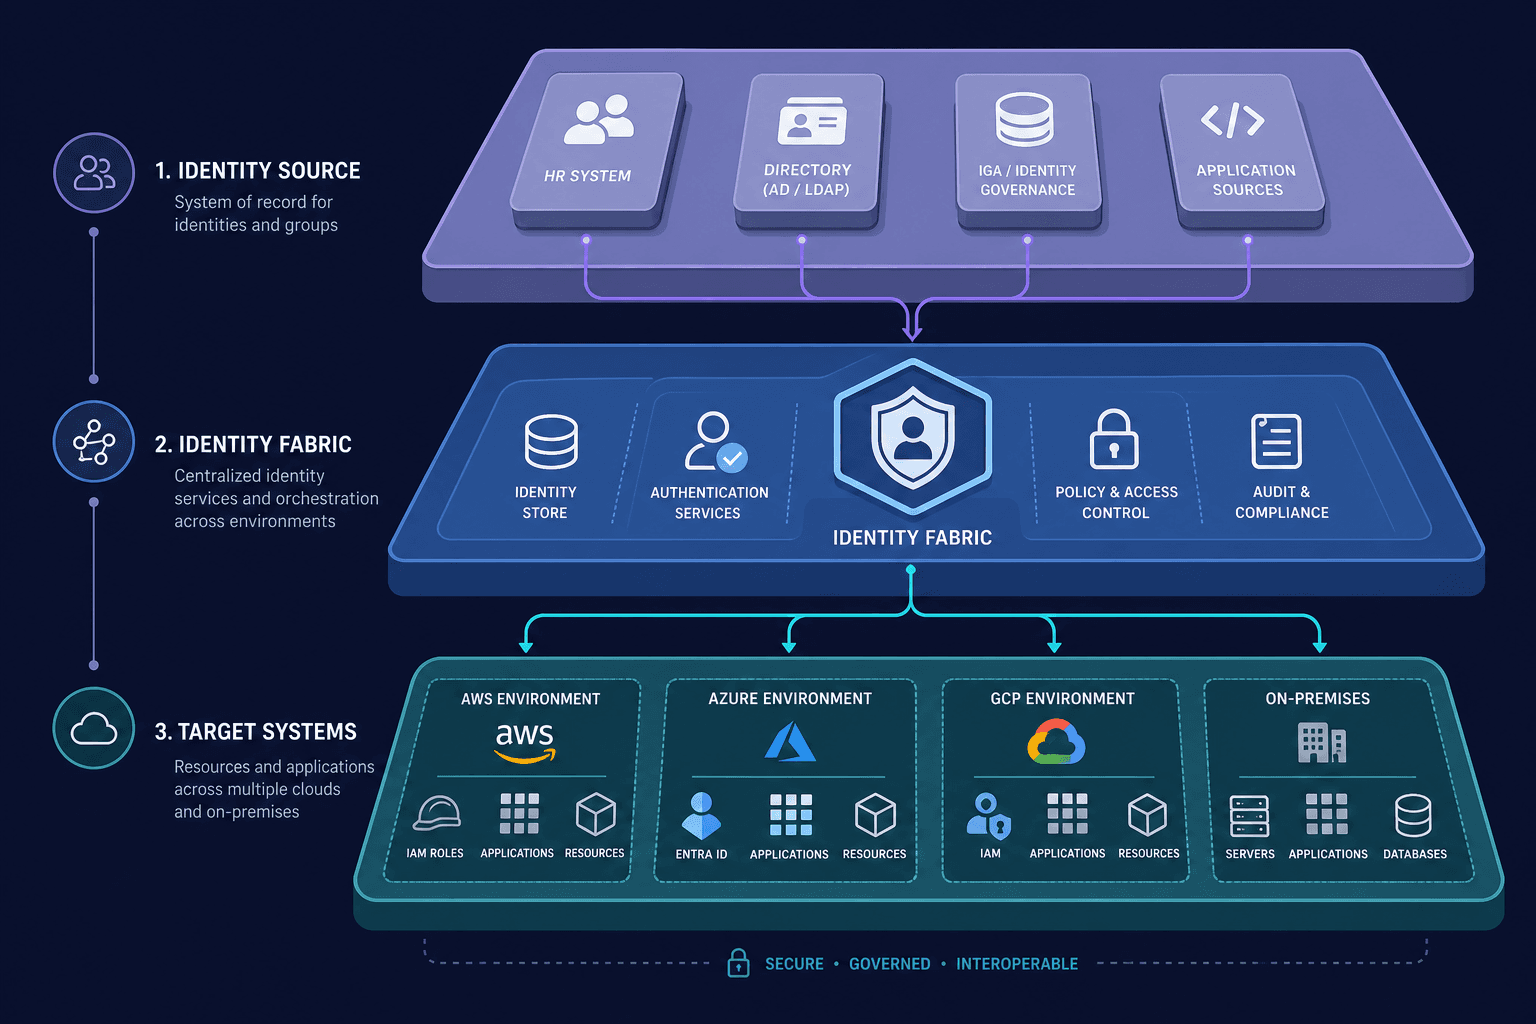
Part 3 · Multi-Cloud IdentityExplore a structured reference framework for cross-cloud IAM, focusing on multi-cloud identity management, entitlements, and reference architecture.
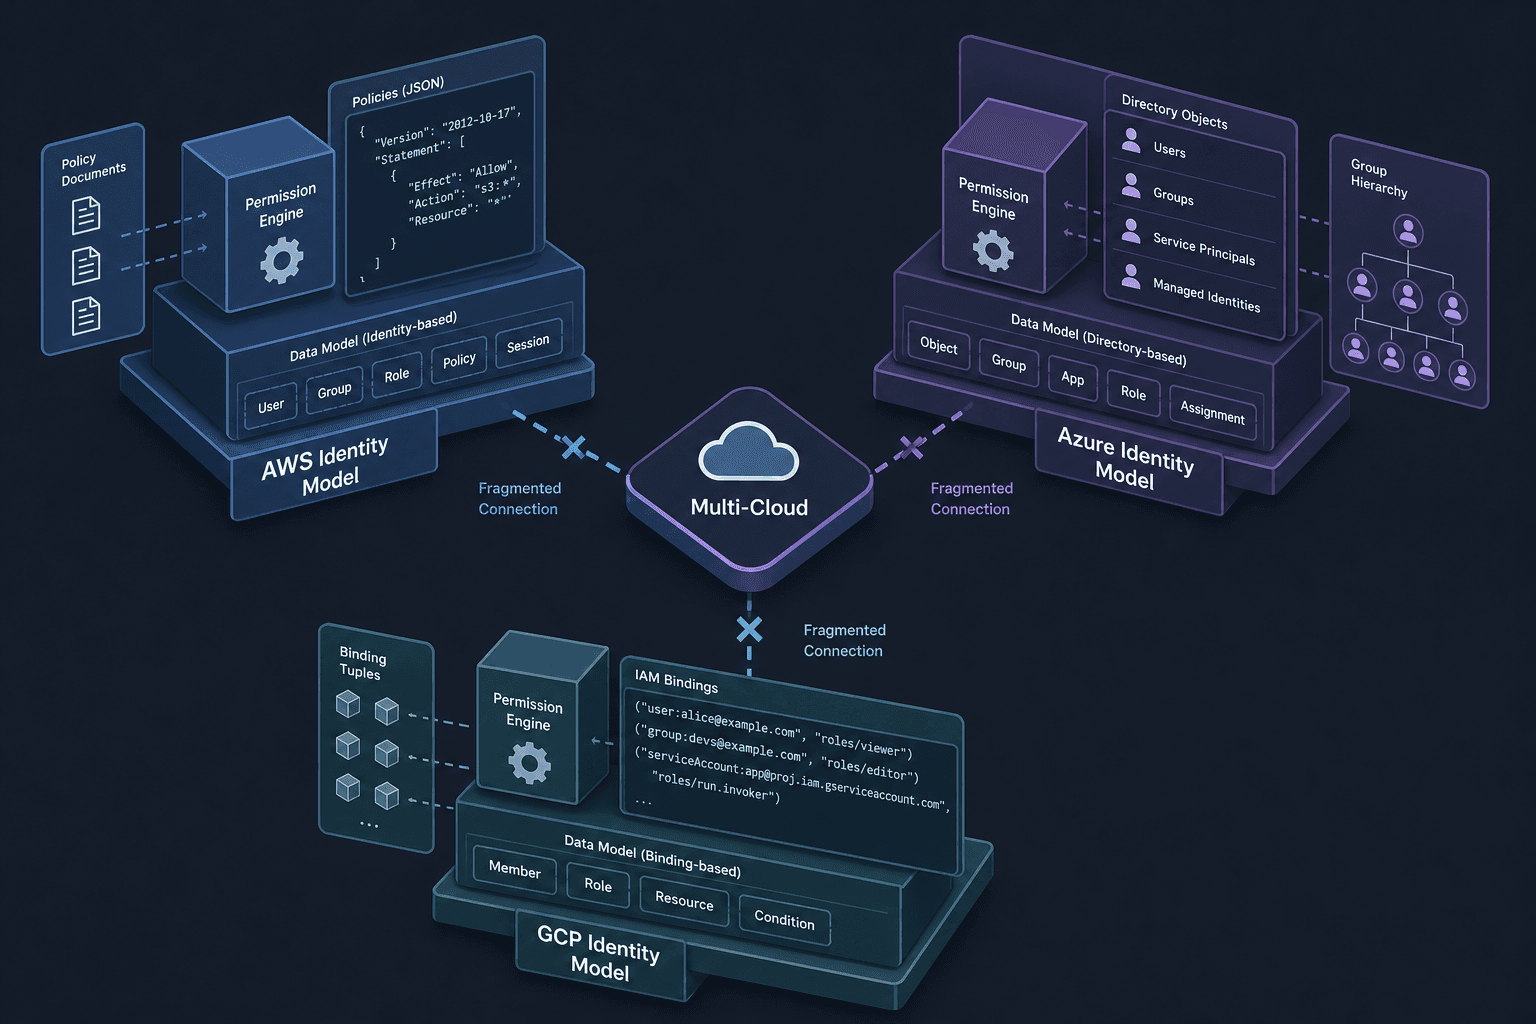
Part 2 · Multi-Cloud IdentityMulti-cloud environments often lead to fragmented identity management. This post compares AWS, Azure, and GCP identity models to highlight key architectural differences.
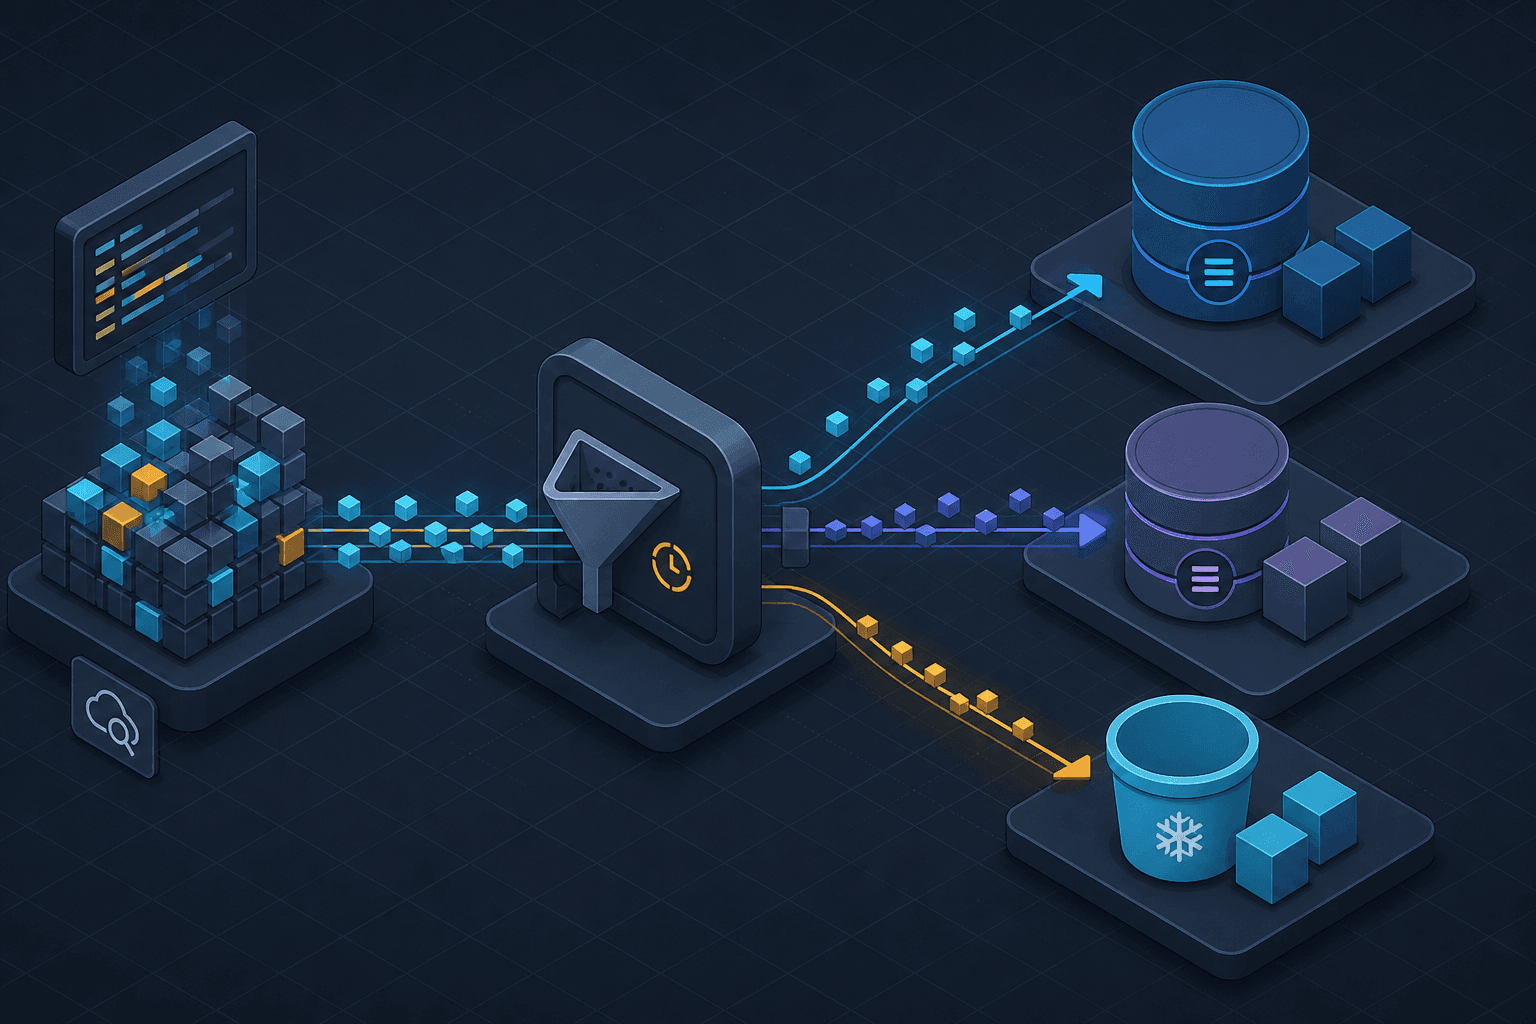
Part 1 · Multi-Cloud IdentityLearn how to optimize AWS logging expenses by configuring CloudWatch Logs retention policies, selecting appropriate log classes, and leveraging S3 tiering.
Part 4 · AWS Security Observability