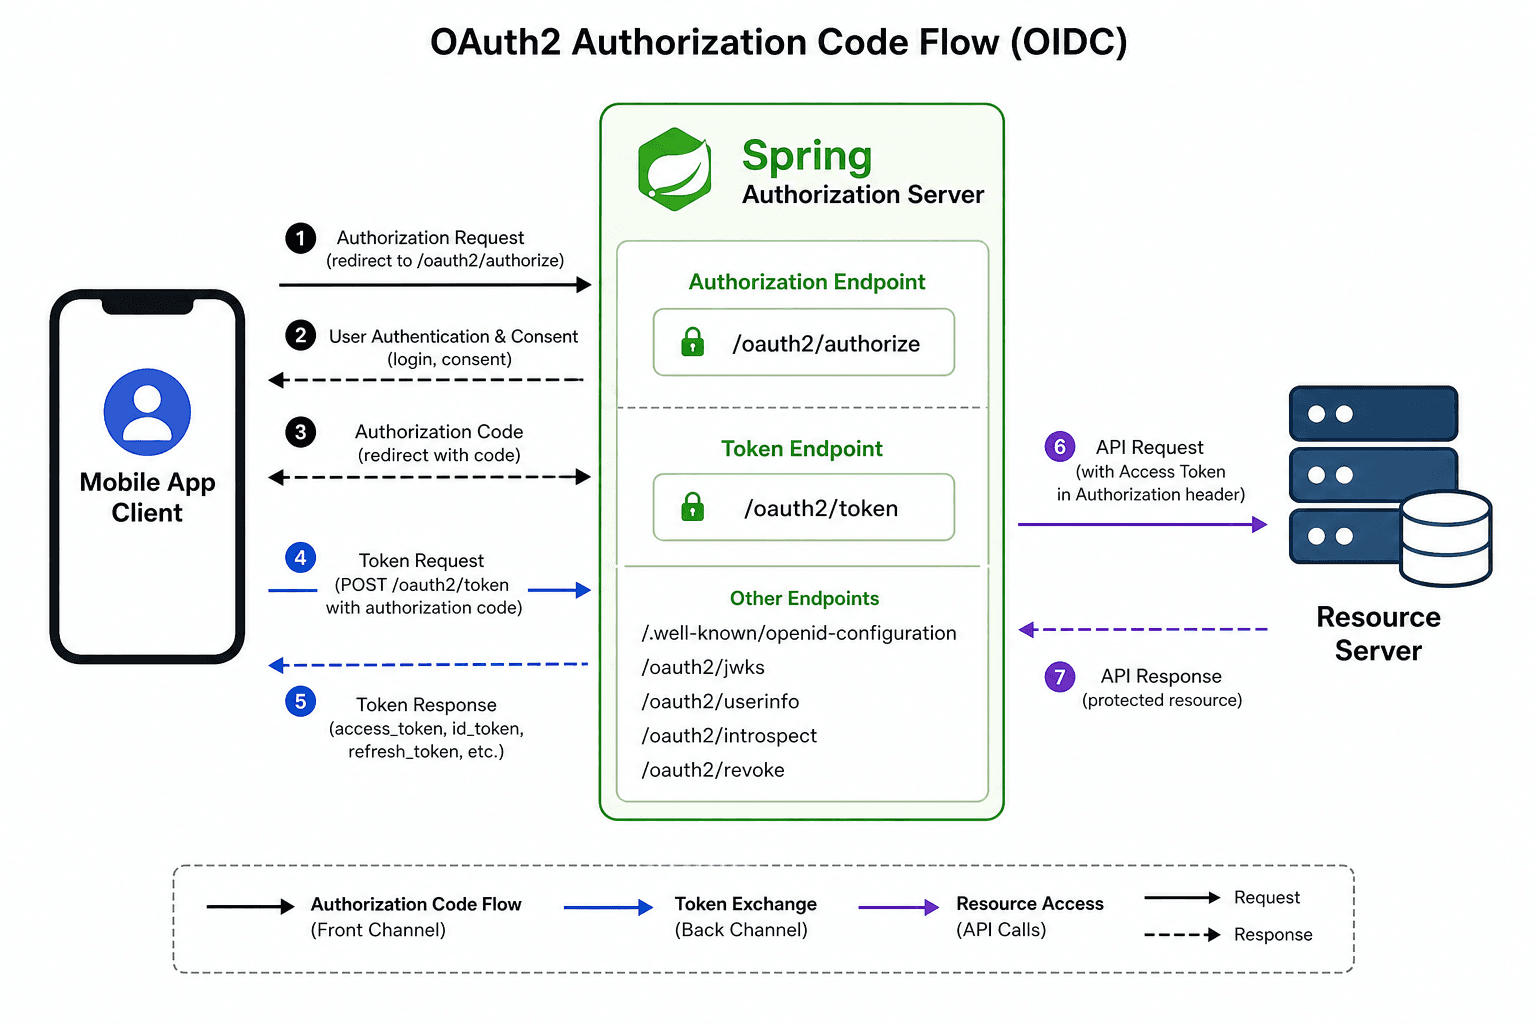
Building a Custom OIDC Provider with Spring Authorization Server
A walkthrough on implementing a custom OIDC provider with Spring Authorization Server, covering setup and configuration details.
Part 5 · OpenID Connect Deep Dive SeriesBlog
Practical guides on OAuth 2.0, OpenID Connect, SAML, Keycloak, and the platform engineering behind identity systems.
595 posts · page 30 of 30
A walkthrough on implementing a custom OIDC provider with Spring Authorization Server, covering setup and configuration details.
Part 5 · OpenID Connect Deep Dive SeriesA technical examination of handling OIDC tokens securely, covering access token lifecycles, refresh mechanisms, and best practices for caching and revocation.
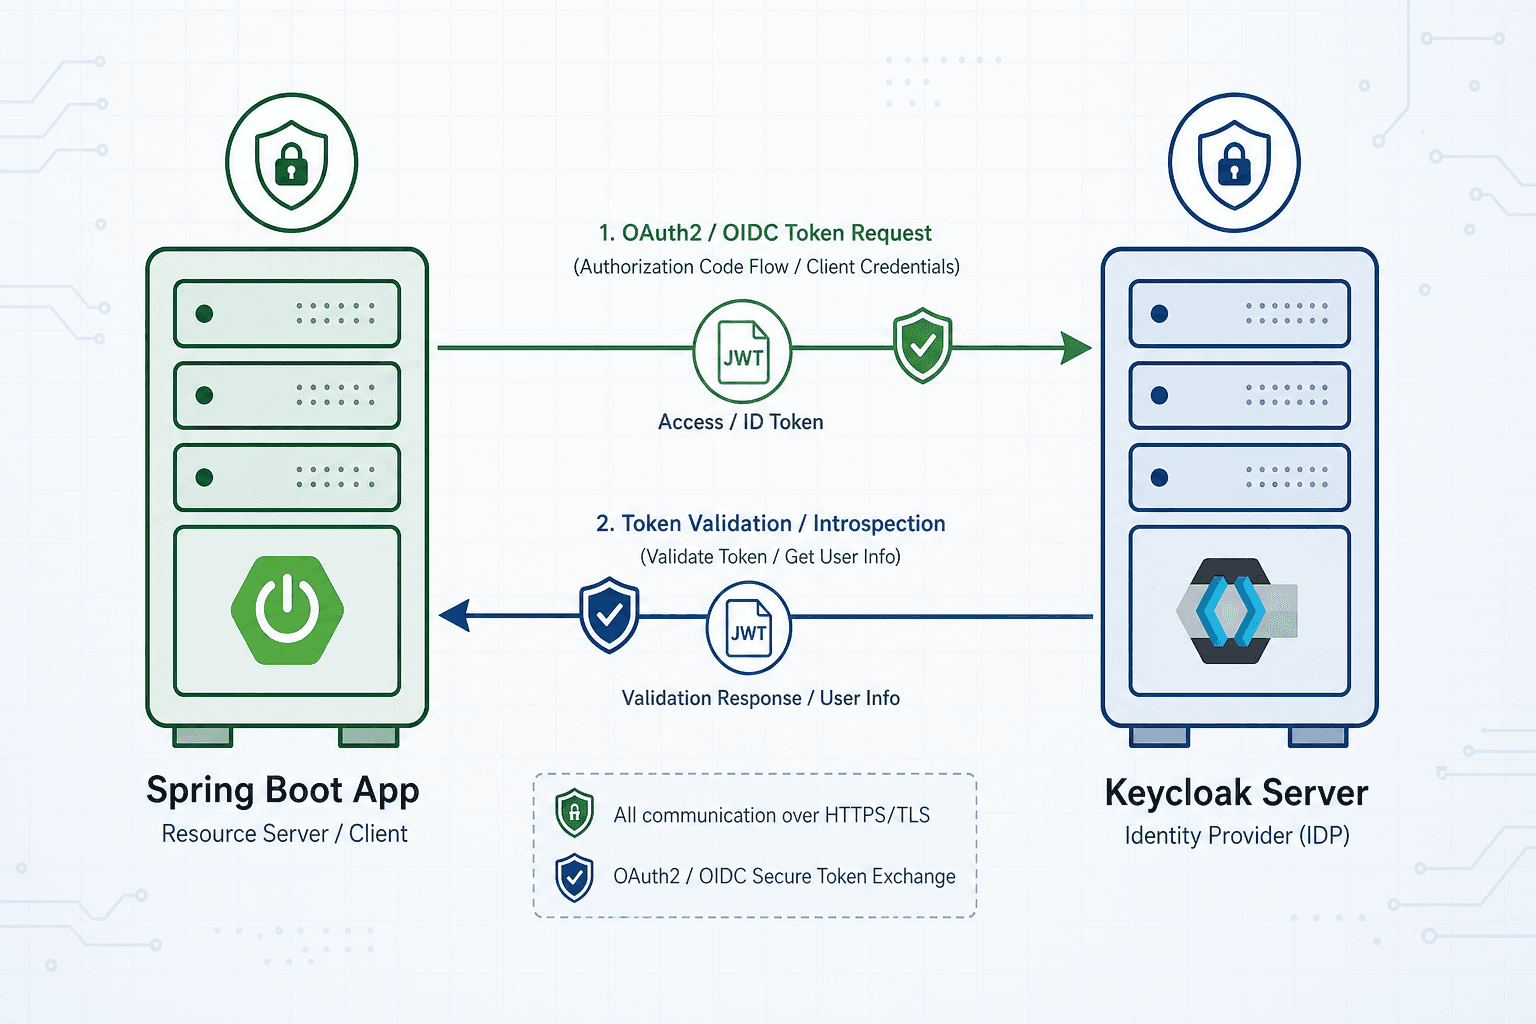
Part 4 · OpenID Connect Deep Dive SeriesLearn how to integrate OpenID Connect authentication into your Spring Boot application using Keycloak for secure user management.
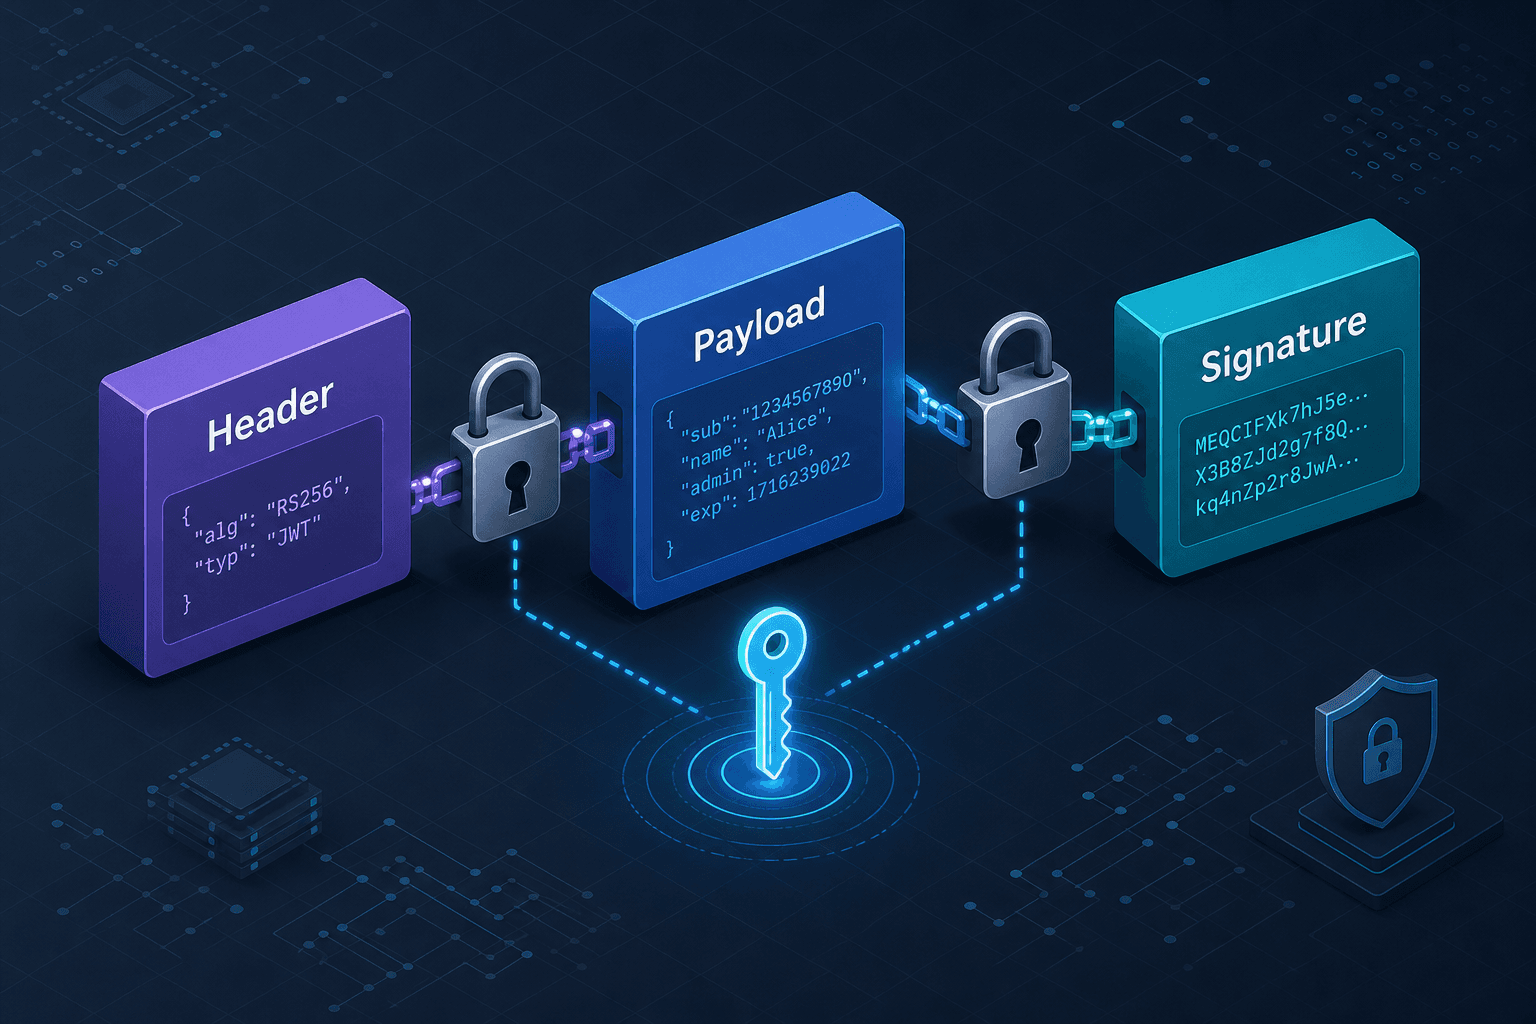
Part 3 · OpenID Connect Deep Dive SeriesExplore the core components of JSON Web Tokens, including JWS and JWE, and learn how to properly sign and validate them for secure applications.
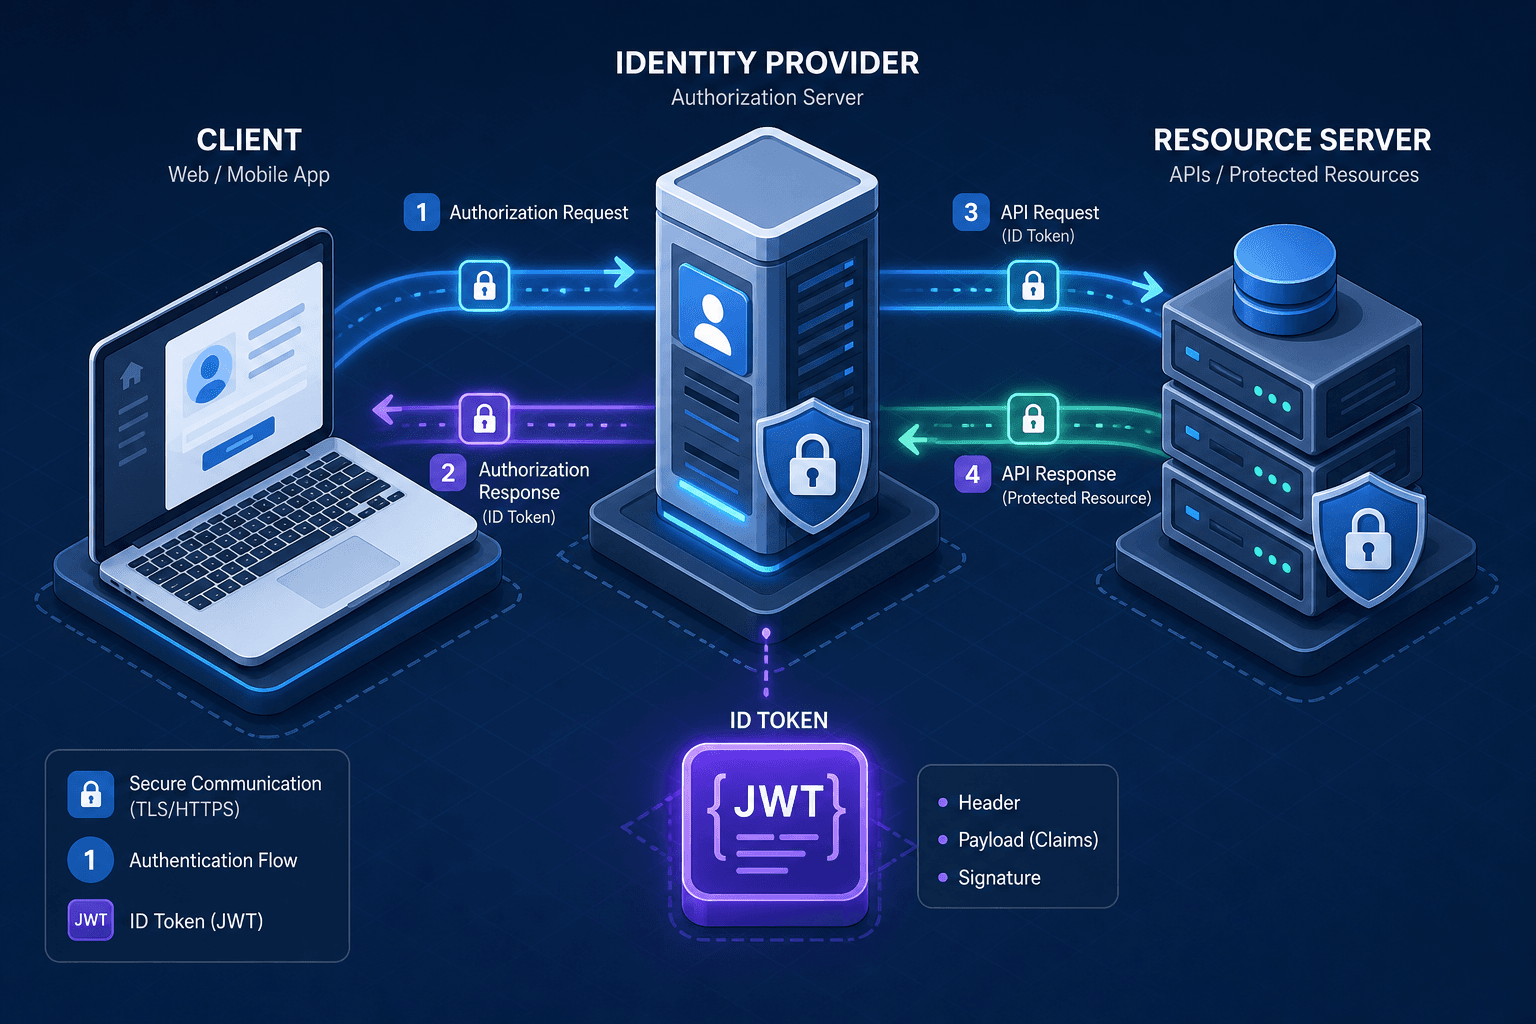
Part 2 · OpenID Connect Deep Dive SeriesUnderstand how OpenID Connect (OIDC) builds on OAuth 2.0 to provide identity solutions, covering ID tokens, discovery mechanisms, and essential flows.
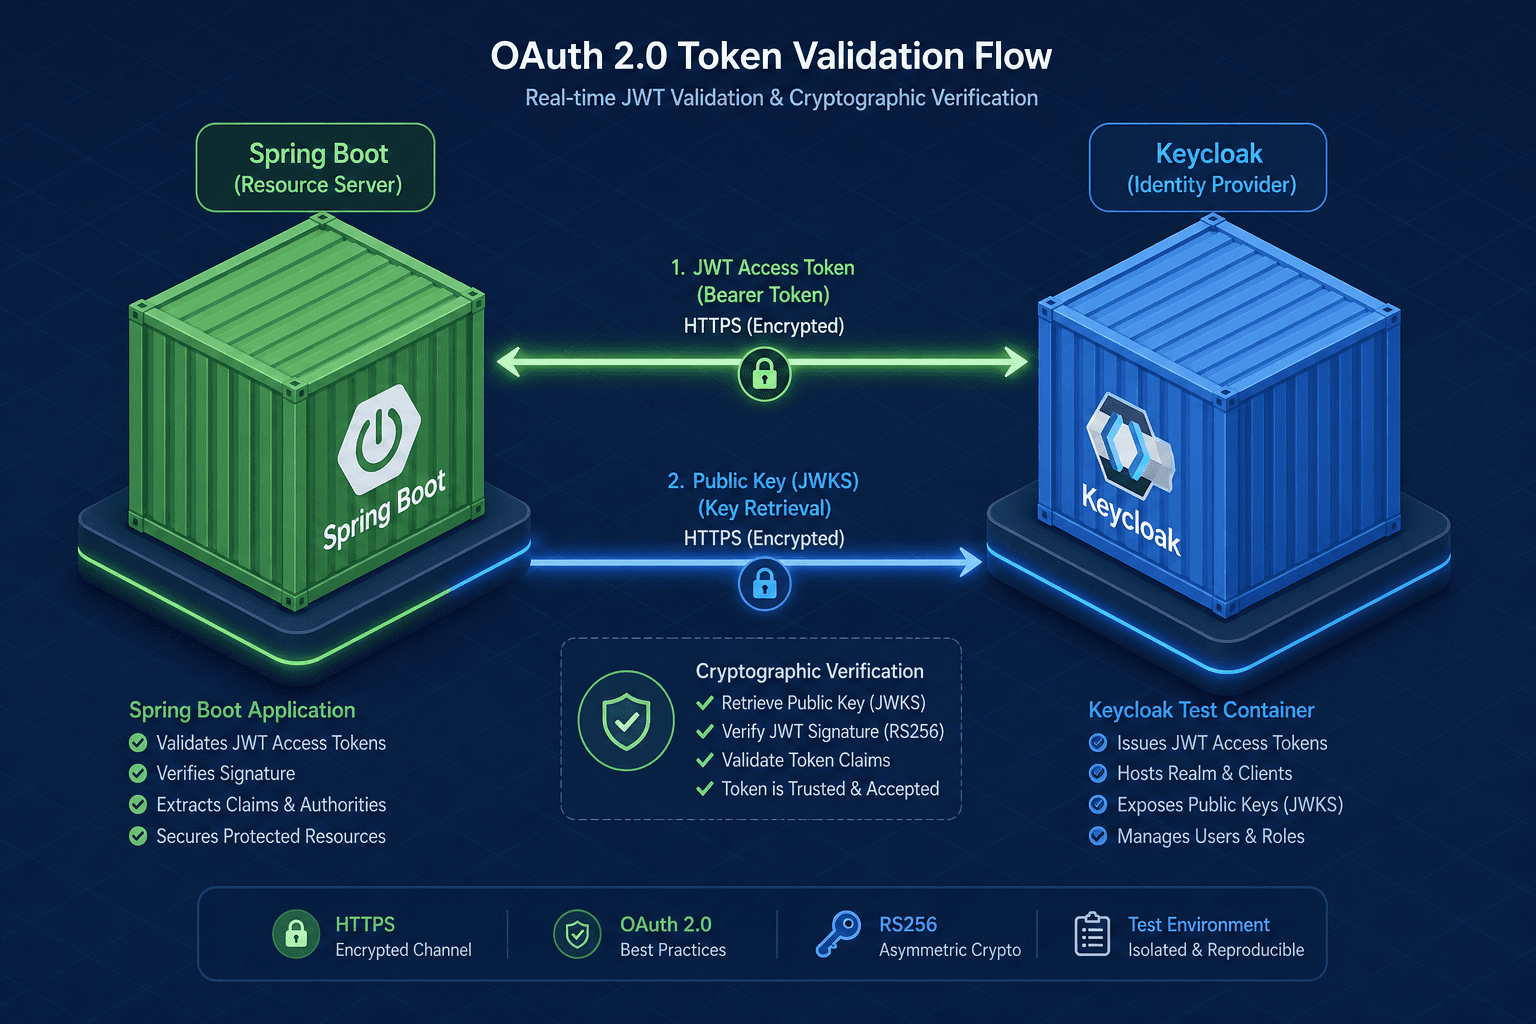
Part 1 · OpenID Connect Deep Dive SeriesLearn how to effectively test OAuth 2.0 integrations with Spring Boot and Keycloak test containers in this technical walkthrough for developers.
Part 10 · OAuth 2.0 Deep Dive SeriesLearn how to secure OAuth 2.0 implementations by preventing common vulnerabilities such as CSRF attacks and token leakage through proven hardening techniques.
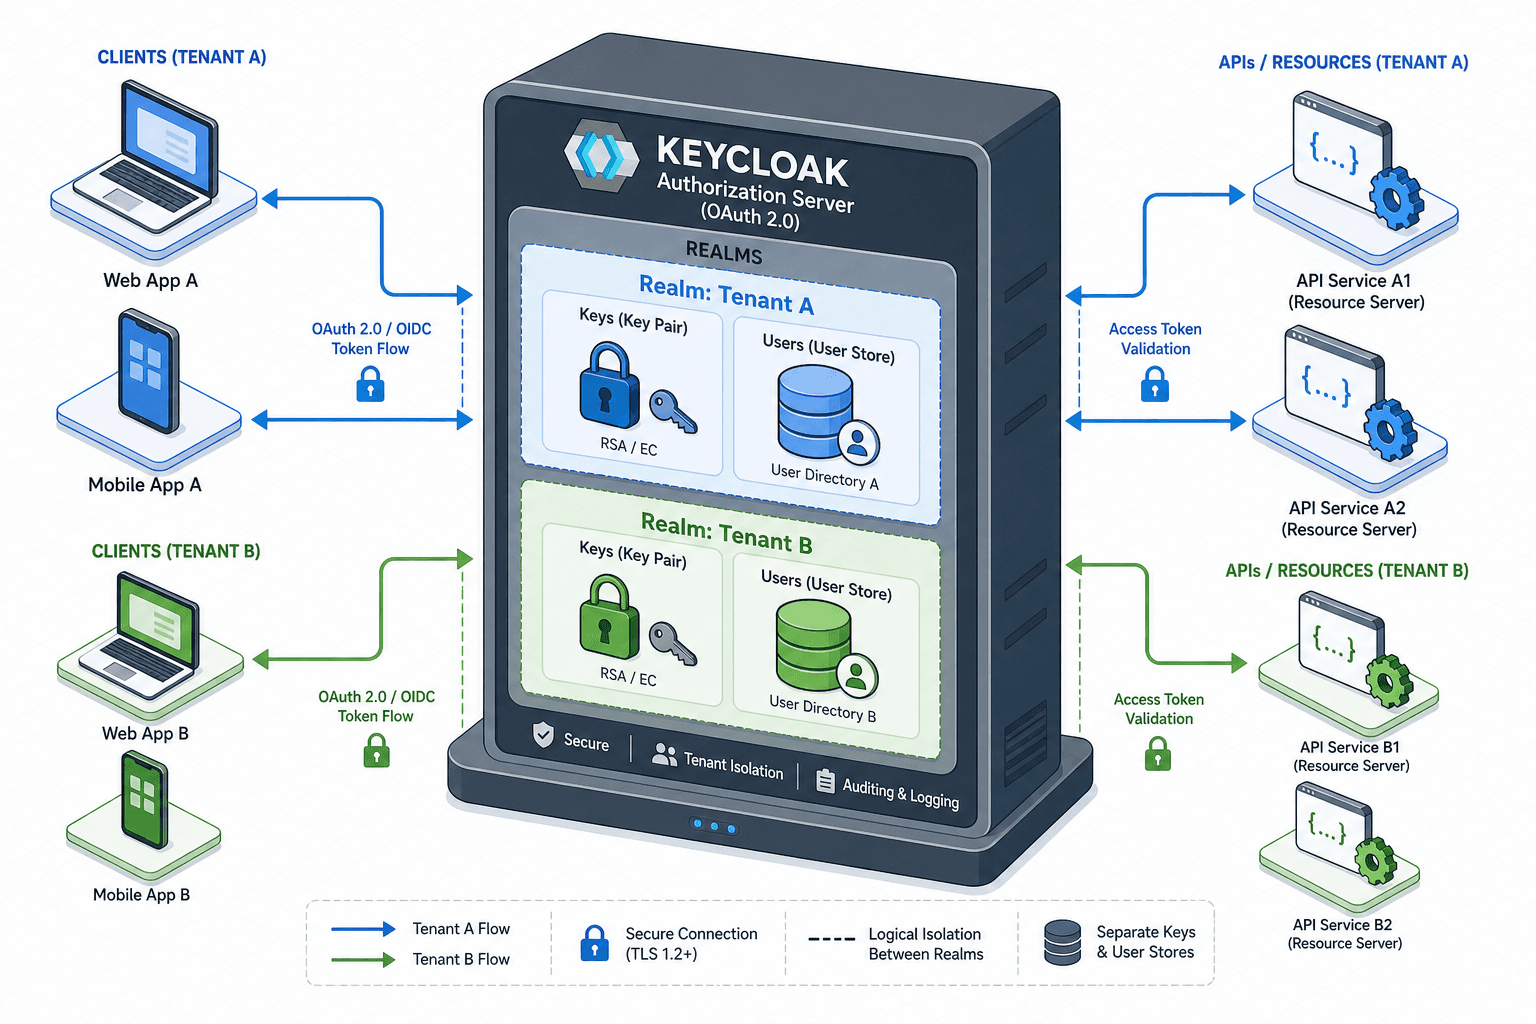
Part 9 · OAuth 2.0 Deep Dive SeriesLearn how to architect a production-ready multi-tenant OAuth 2.0 authorization server using Keycloak, ensuring secure tenant isolation for SaaS applications.
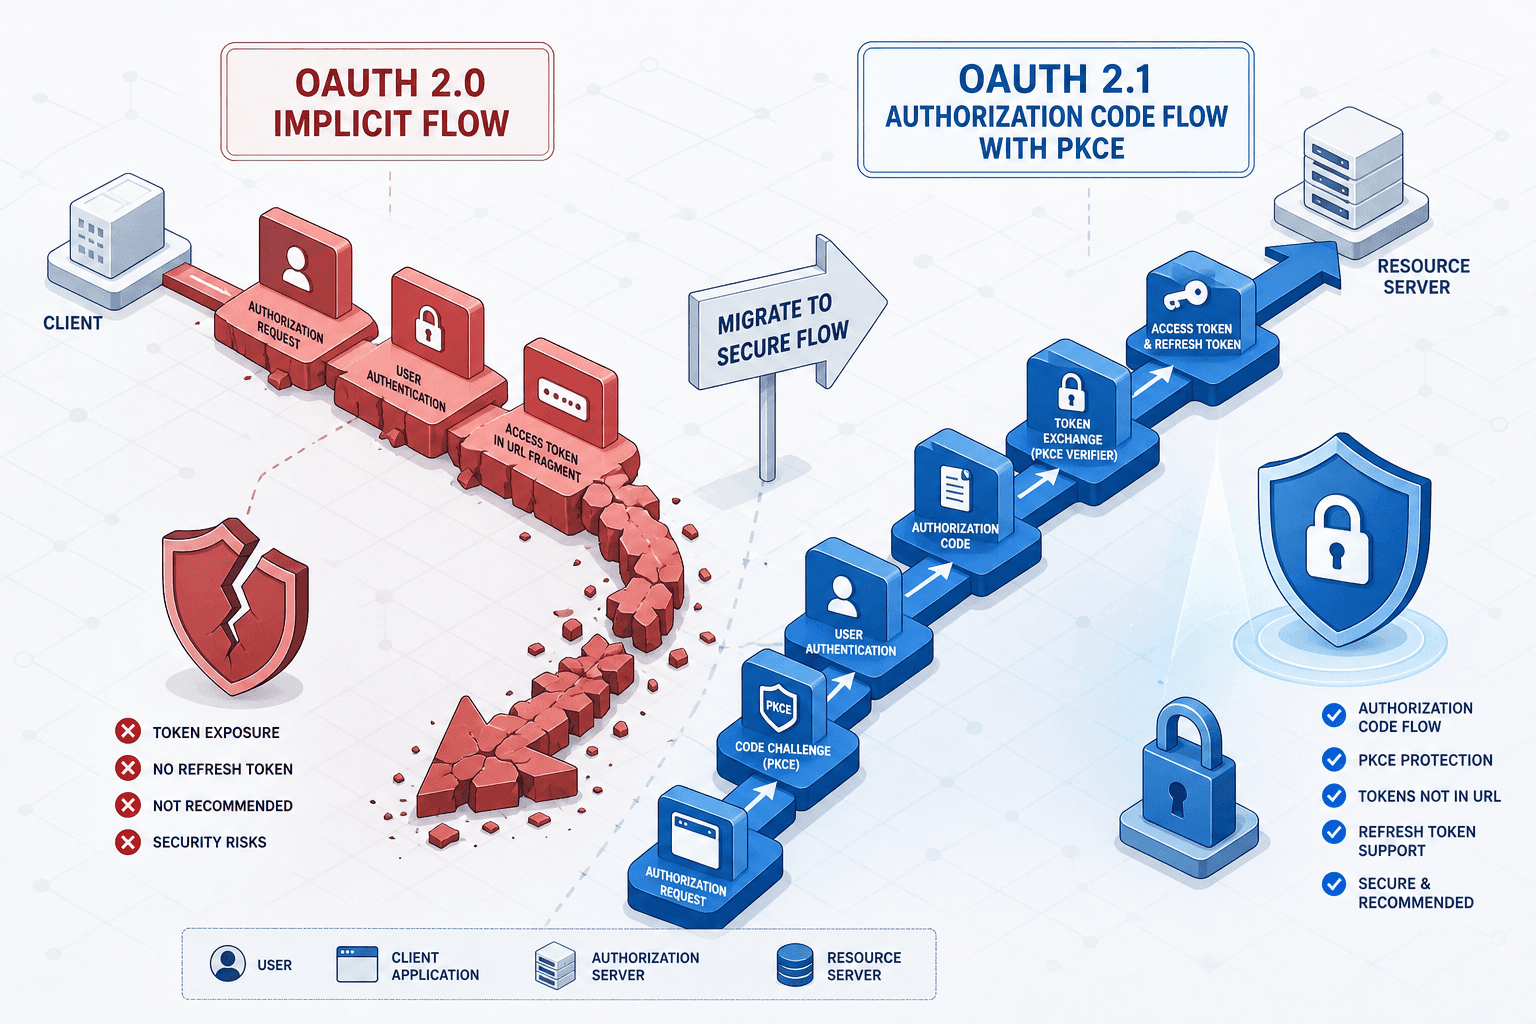
Part 8 · OAuth 2.0 Deep Dive SeriesLearn how to prepare for OAuth 2.1 with mandatory PKCE, key deprecations, and essential security updates for a secure transition.
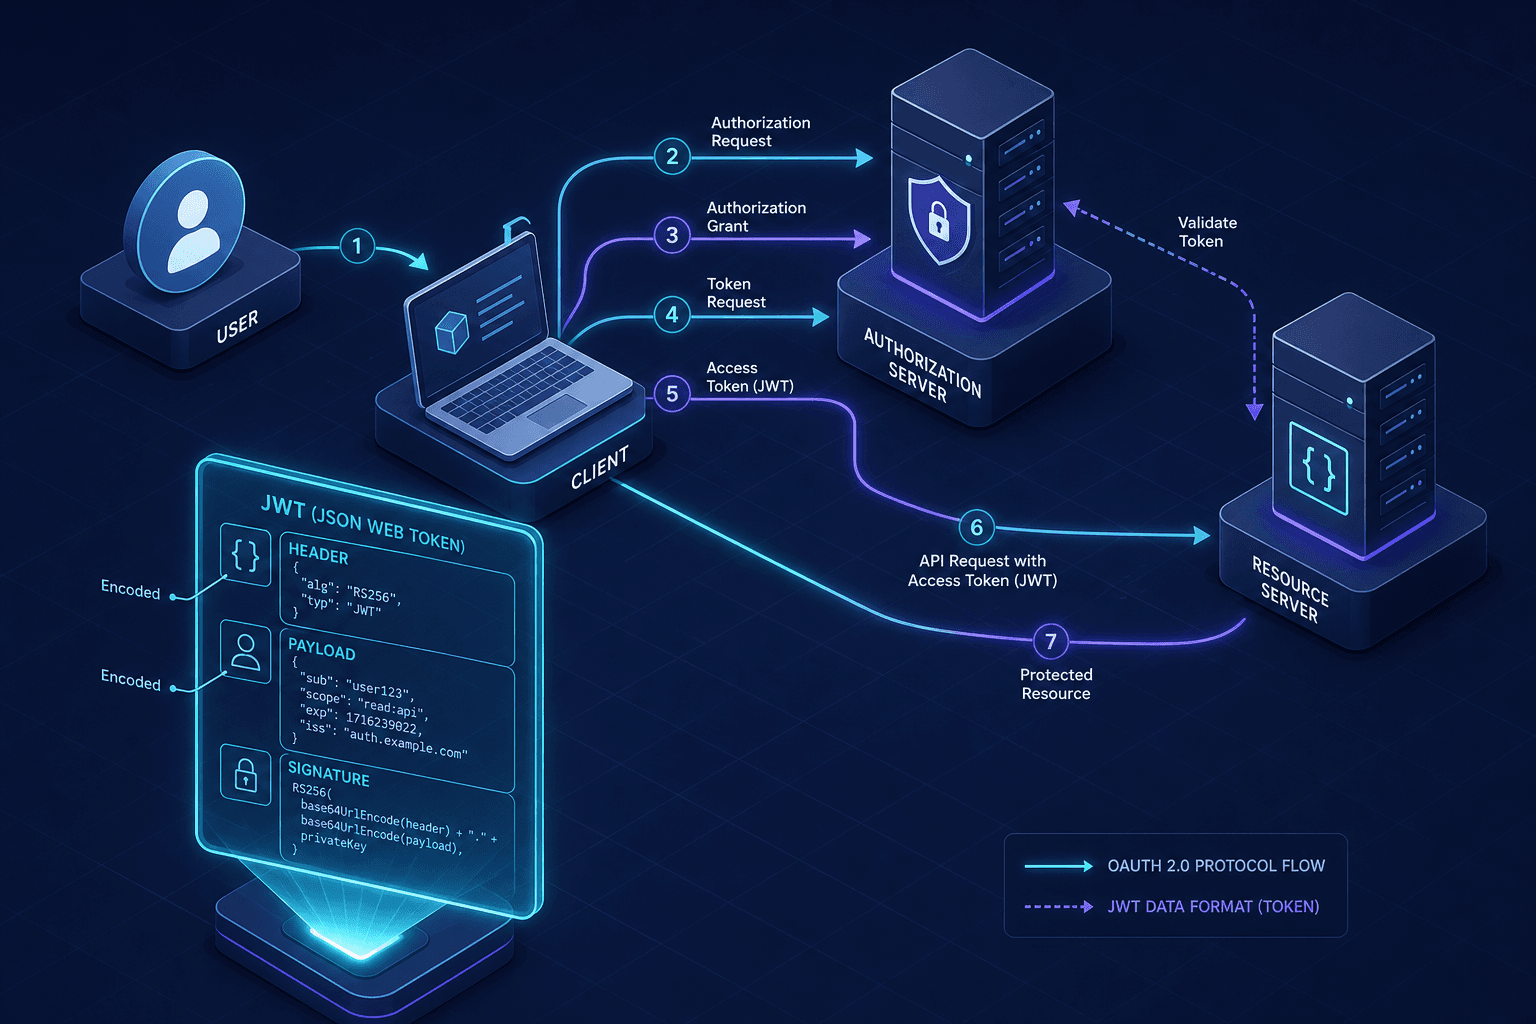
Part 7 · OAuth 2.0 Deep Dive SeriesClarify how OAuth 2.0 protocols interact with JSON Web Tokens. Learn about opaque tokens, format selection strategies, and essential best practices for secure implementation.
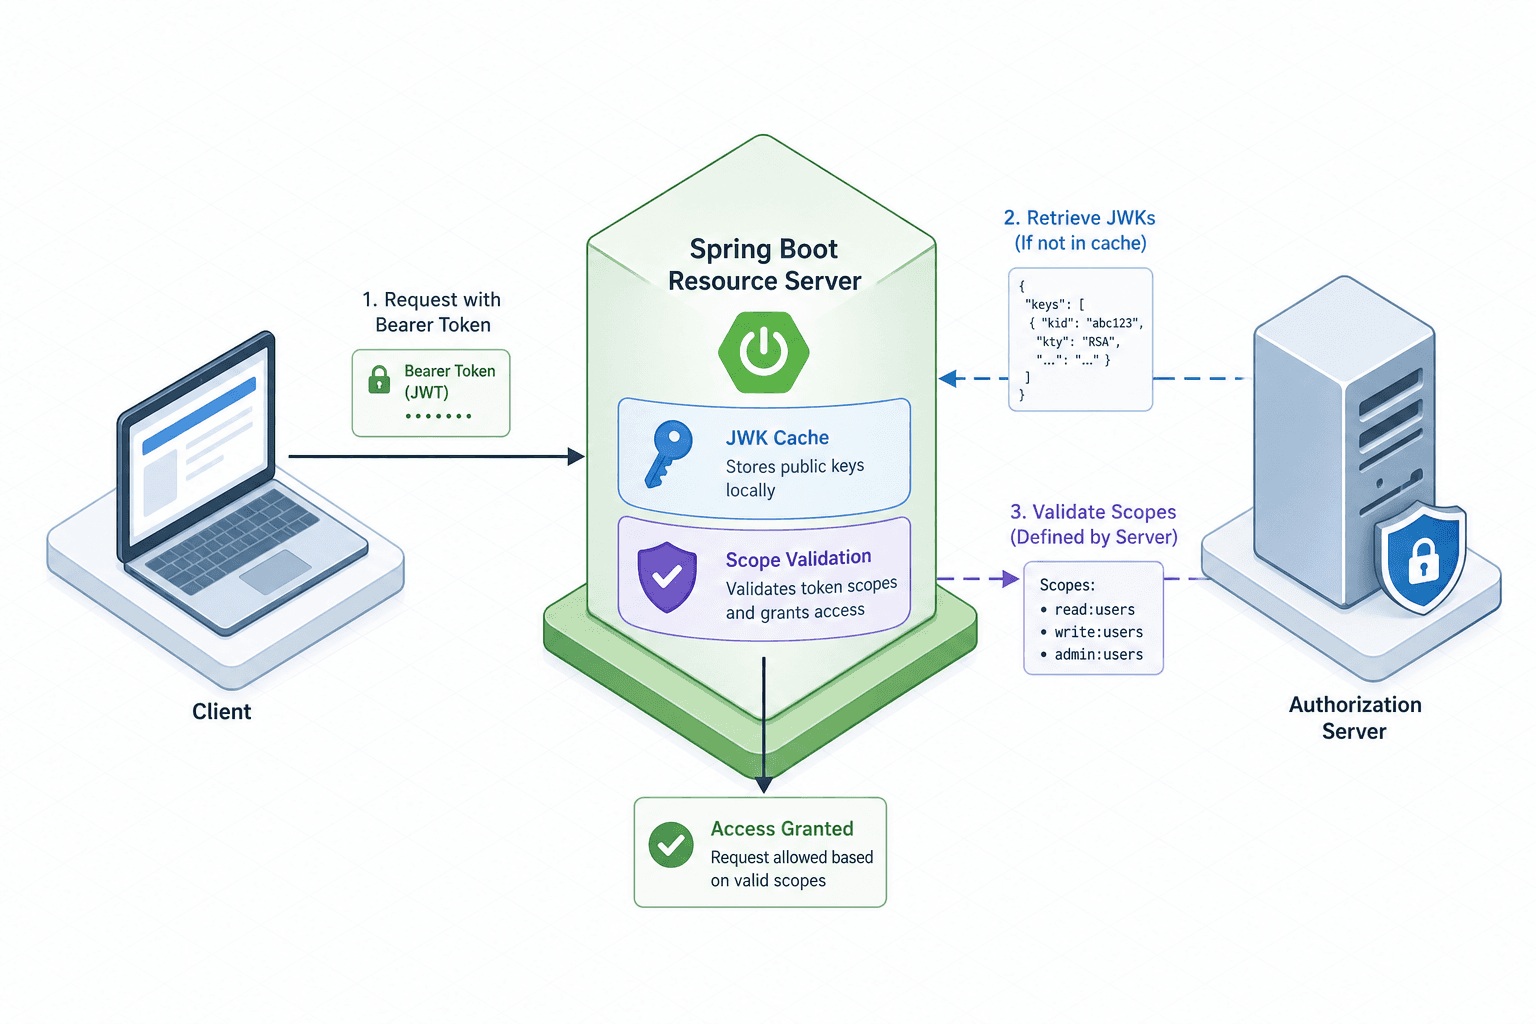
Part 6 · OAuth 2.0 Deep Dive SeriesImplement secure access for your Spring Boot applications by configuring an OAuth 2.0 Resource Server to validate JWT tokens and enforce scope-based access control.
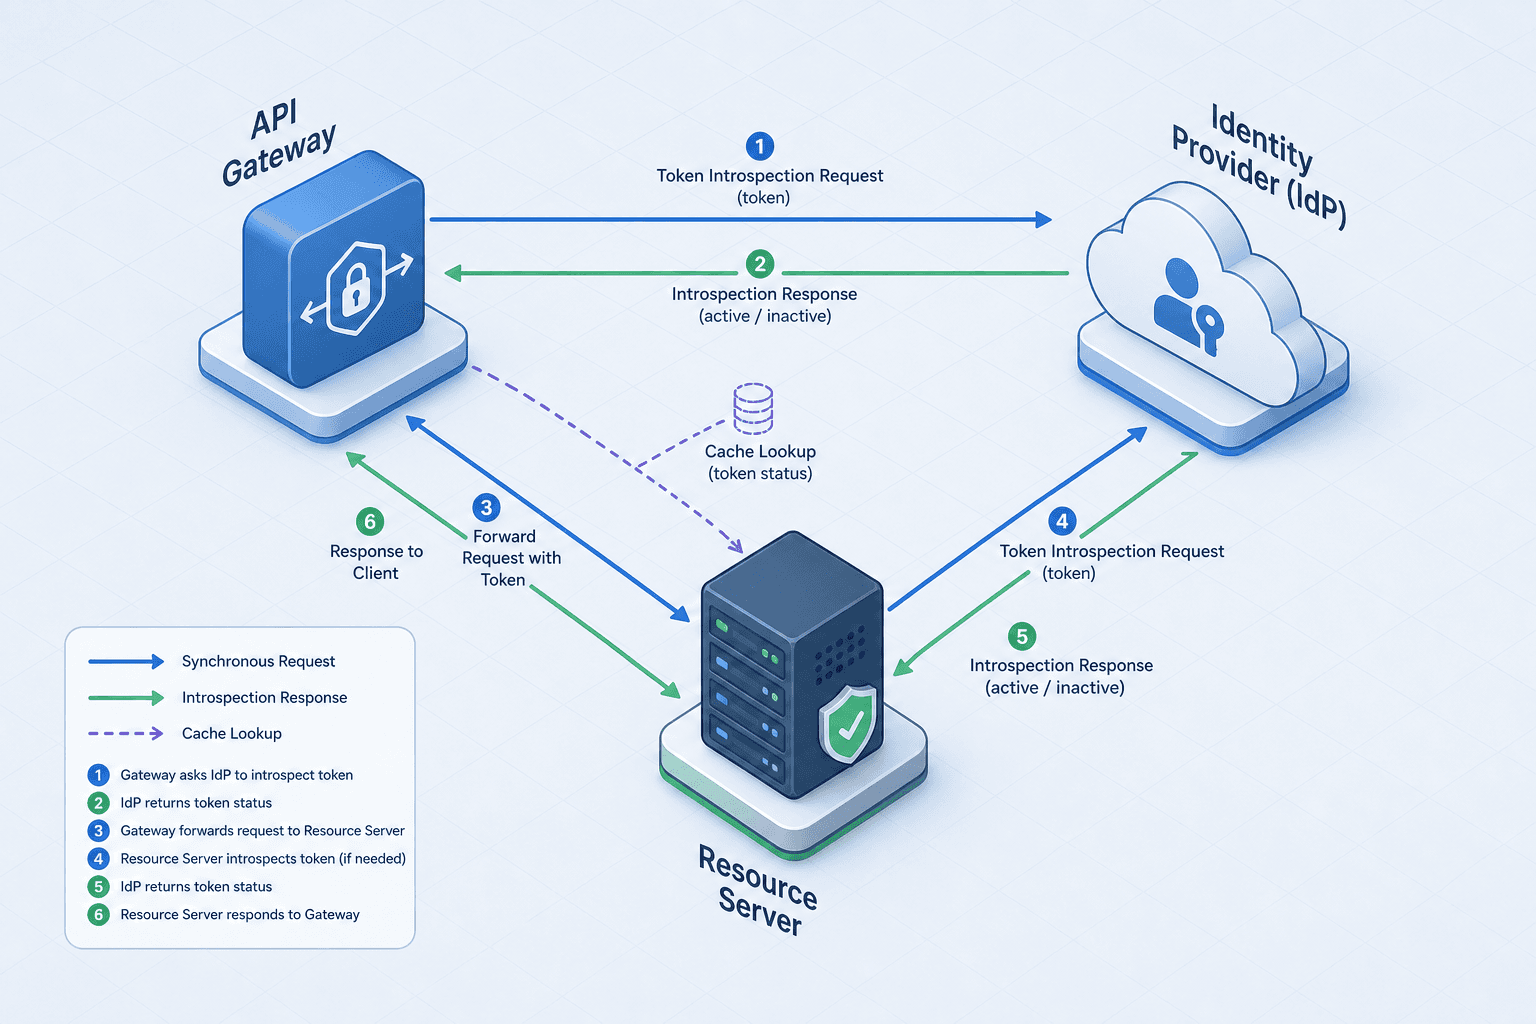
Part 5 · OAuth 2.0 Deep Dive SeriesExplore production-grade approaches to managing token lifecycles, implementing introspection endpoints, and enforcing revocation policies in secure environments.
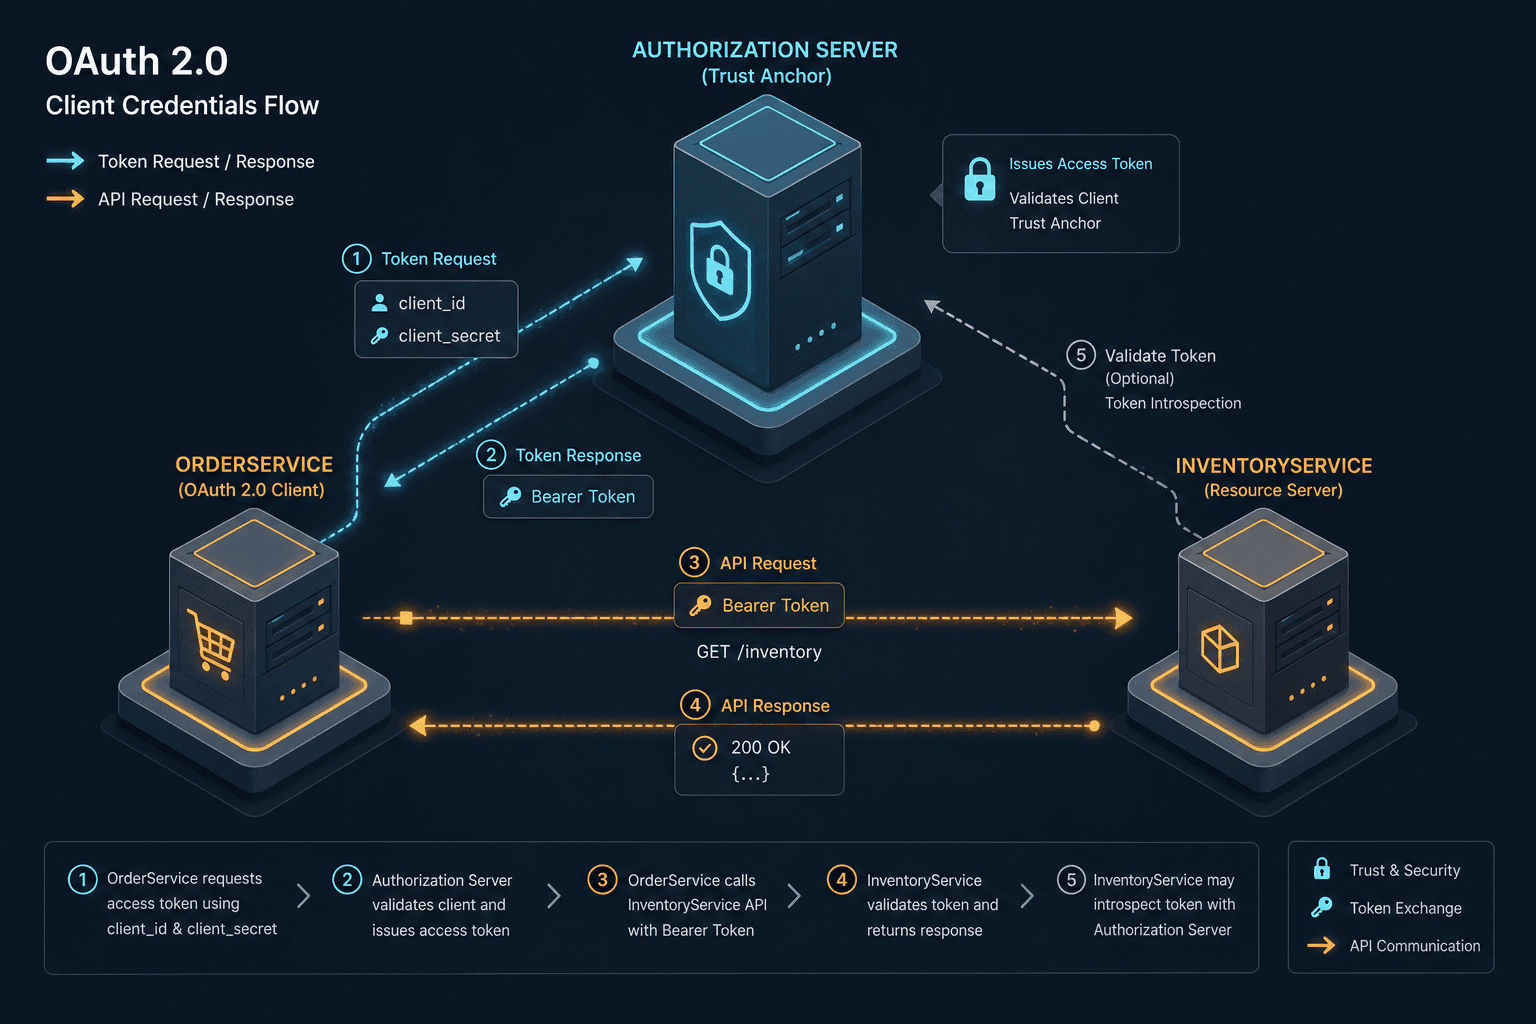
Part 4 · OAuth 2.0 Deep Dive SeriesLearn how to implement the OAuth 2.0 client credentials flow for secure service-to-service communication using Spring Boot OAuth2.
Part 3 · OAuth 2.0 Deep Dive SeriesLearn how to implement the OAuth 2.0 Authorization Code Flow with PKCE to secure Single Page Applications and mobile apps against interception attacks.
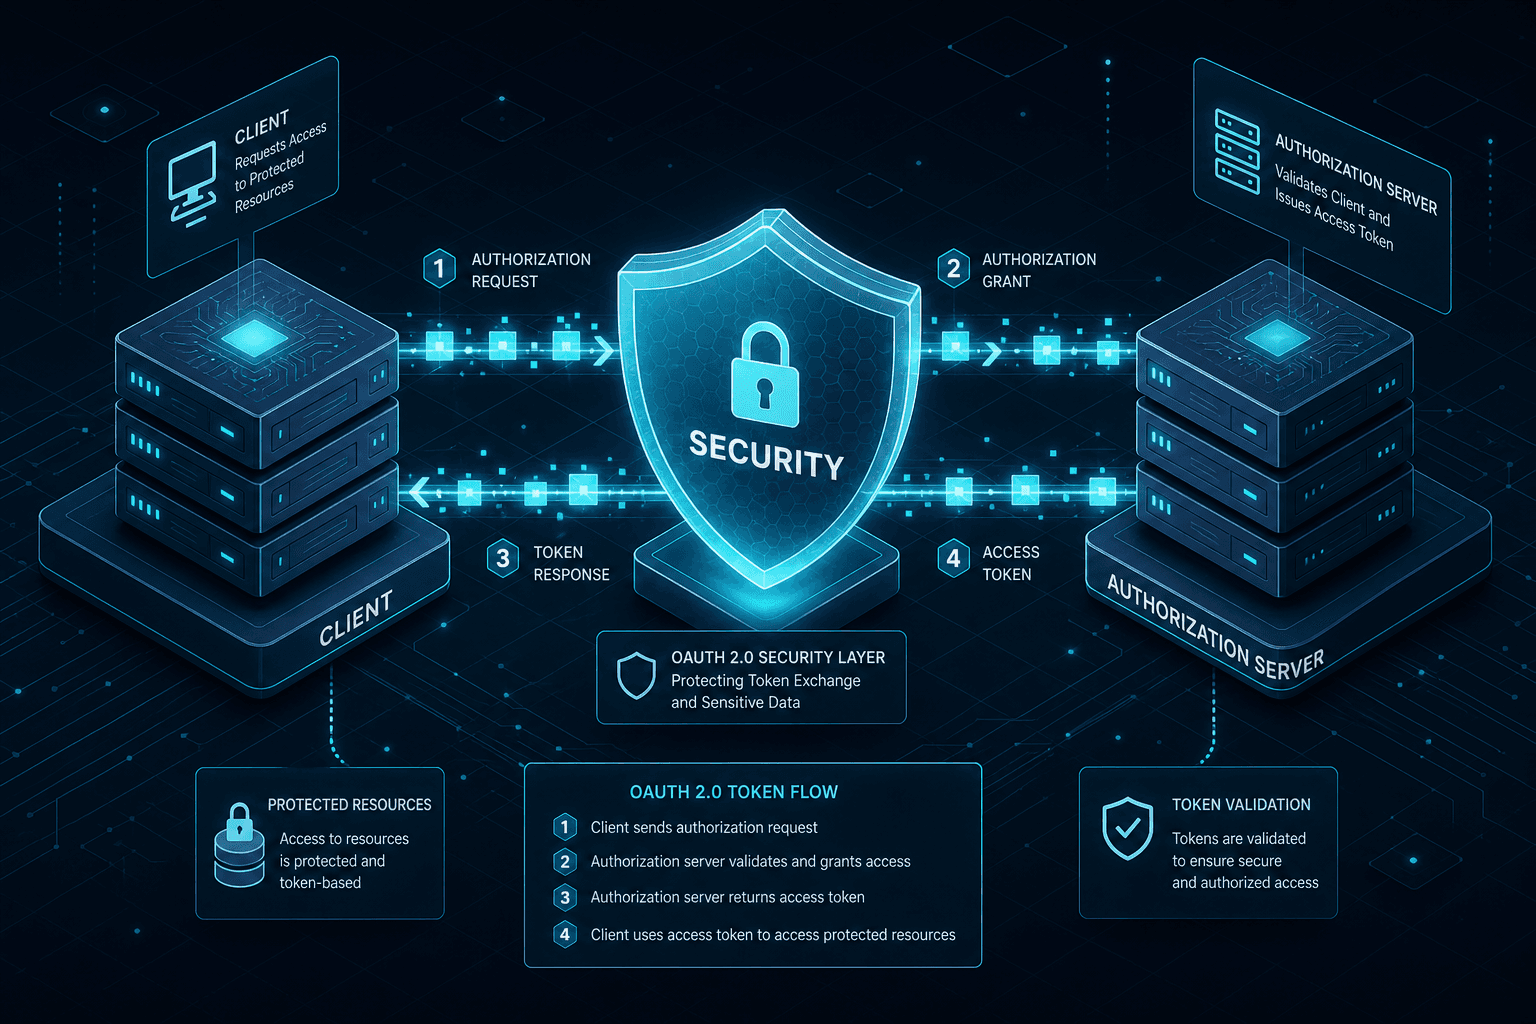
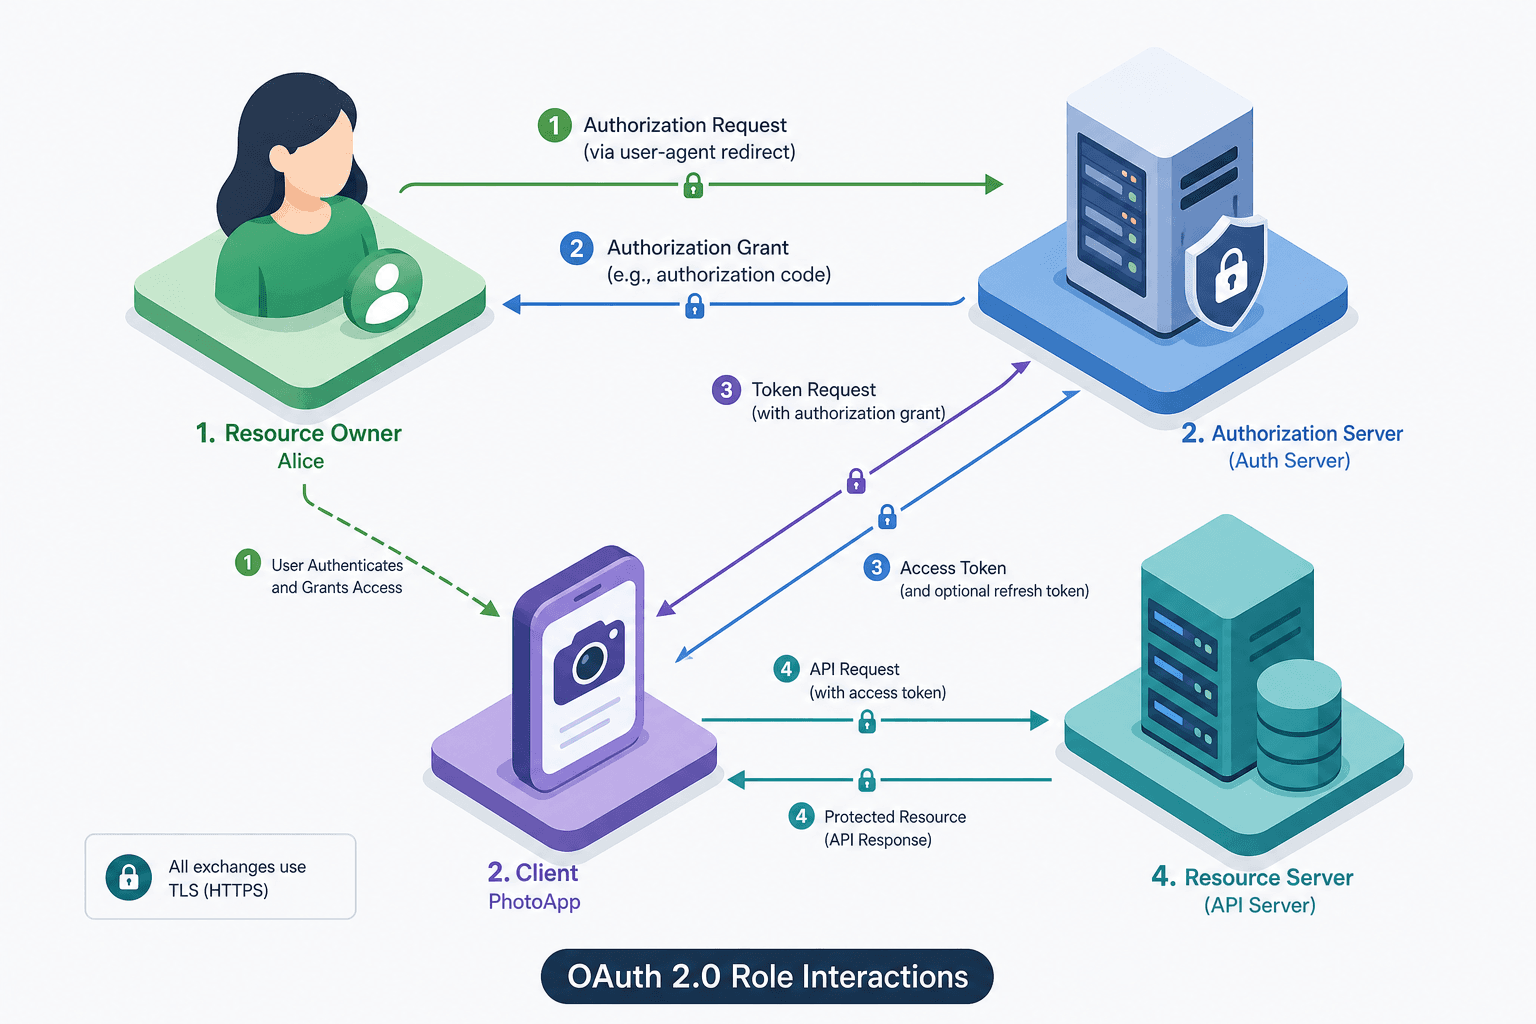
Part 2 · OAuth 2.0 Deep Dive SeriesUnderstand the core components of OAuth 2.0.
Part 1 · OAuth 2.0 & OIDC Mastery